

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Hacker Conversations: Corey Thuen and the Evil Bit

    October 22, 2026

    Saipem and Egypt’s MDC seal pact to target MENA offshore drilling market

    October 22, 2026

    Nature Can’t Wait by Mary Robinson

    October 22, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Hacker Conversations: Corey Thuen and the Evil Bit
    • Saipem and Egypt’s MDC seal pact to target MENA offshore drilling market
    • Nature Can’t Wait by Mary Robinson
    • What update to Meta’s terms for business accounts says about AI scraping
    • Germany arrests Ukrainian national on suspicion of spying for Russia
    • UK must prepare for infrastructure attacks by hostile states, says Streeting | Infrastructure
    • Amazon says PHP2Shell exploitation began 4 days before patches
    • Oxford scientists discover how viruses build themselves without a blueprint
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, October 22
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    GitLab warns of new max severity code execution vulnerability

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 22, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    GitLab has released security patches for a maximum-severity Regular Expression Compiler flaw that can let remote attackers run arbitrary code on vulnerable servers.

    This security issue is tracked as CVE-2026-110264 and was reported by a security researcher using the ‘joaxcar‘ handle through GitLab’s HackerOne bug bounty program.

    CVE-2026-110264 stems from an integer overflow weakness in GitLab’s Regular Expression Compiler, a background engine that parses and validates regular expressions in configuration files.

    GitLab has fixed the vulnerability in GitLab Community Edition (CE) and Enterprise Edition (EE) versions 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, and 18.11.13, and warned users to patch their instances immediately.

    “GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary code on the GitLab server due to integer overflow when compiling a specially crafted regular expression,” the company said.

    “We strongly recommend that all installations running a version affected by the issues described below are upgraded to the latest version as soon as possible. [..] GitLab.com is already running the patched version. GitLab Dedicated tenants running 19.3.5-internal0 and 19.4.2-internal0 or later already include these fixes and do not need to take action.”

    Internet threat watchdog Shadowserver now tracks over 2,700 GitLab Community Edition instances exposed online, but it doesn’t provide any information about how many of them are honeypots or have already been secured against attacks.
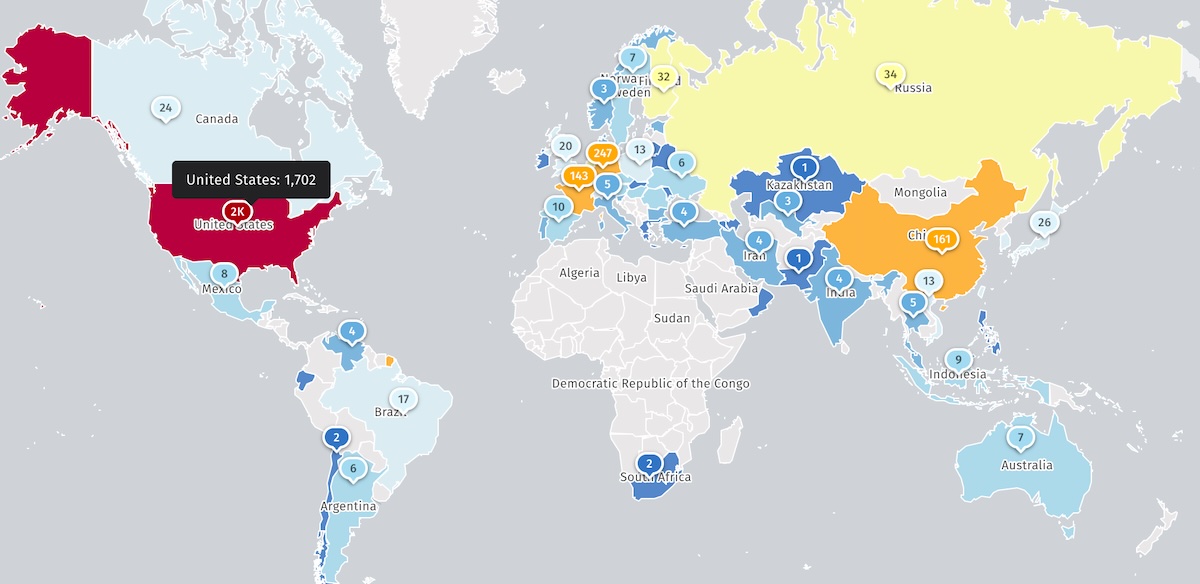
    Internet-exposed GitLab CE instances
    Internet-exposed GitLab CE instances (Shadowserver)

    GitLab warned customers ten days ago about another critical remote code execution vulnerability (CVE-2026-97229) with a 10/10 CVSS base score in the CI/CD Regular Expression Compiler, reported by the same security researcher.

    Last month, it fixed another maximum-severity GitLab CE/EE flaw (CVE-2026-85706) that lets unauthenticated attackers read sensitive data (e.g., credentials and other secrets) from vulnerable servers.

    One day later, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-85706 to its list of actively exploited flaws and ordered federal agencies to secure their systems within three days.

    Since November 2021, CISA has flagged five GitLab flaws used in the wild, including one exploited in ransomware attacks.

    GitLab’s DevSecOps platform has over 30 million registered users worldwide and is used by over 50% of Fortune 100 companies, including Nvidia, T-Mobile, Lockheed Martin, Airbus, and Goldman Sachs.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    Code Execution GitLab Max severity Vulnerability warns
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Hacker Conversations: Corey Thuen and the Evil Bit

    Amazon says PHP2Shell exploitation began 4 days before patches

    Splunk, SolarWinds Release Fresh Security Updates

    Japan’s Onamae Desktop Cloud hacked, up to 27,000 servers affected

    LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release

    Serious risks at EU borders, fundamental rights agency warns – POLITICO

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Hacker Conversations: Corey Thuen and the Evil Bit

    October 22, 2026

    Saipem and Egypt’s MDC seal pact to target MENA offshore drilling market

    October 22, 2026

    Nature Can’t Wait by Mary Robinson

    October 22, 2026

    What update to Meta’s terms for business accounts says about AI scraping

    October 22, 2026
    Latest Posts

    Big Bear Valley’s beloved bald eagle Jackie is dead

    August 14, 2026

    Cascade Volcanoes Shrouded in Smoke

    August 14, 2026

    Bit Digital pledged 74% of its staked Ethereum position to a loan that can trigger a 24-hour collateral call

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Hacker Conversations: Corey Thuen and the Evil Bit

    October 22, 2026

    Saipem and Egypt’s MDC seal pact to target MENA offshore drilling market

    October 22, 2026

    Nature Can’t Wait by Mary Robinson

    October 22, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.