

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Bomb threat forces Tel Aviv to Vienna flight to land in Bulgaria

    October 19, 2026

    Burnham pledges ‘big changes’ to the way the welfare system works to tackle Neets crisis – UK politics live | Politics

    October 19, 2026

    From climate and nature risks to economic resilience and competitiveness

    October 19, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Bomb threat forces Tel Aviv to Vienna flight to land in Bulgaria
    • Burnham pledges ‘big changes’ to the way the welfare system works to tackle Neets crisis – UK politics live | Politics
    • From climate and nature risks to economic resilience and competitiveness
    • Anthropic Acquires Confidential AI Startup Opaque Systems
    • Two monster black holes could collide in just 100 years
    • Companies exploiting welfare system by using residents as ‘cash cows,’ BBC finds
    • My critics think speaking fluently is vital for fee-paying pupils, but not for anyone else. Here’s why I reject that | Lucy Powell
    • The EU heads into a perfect political storm – POLITICO
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Monday, October 19
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Unpatched Broadcom Wi-Fi Flaw Lets Attackers in Range Run Code as Root on Routers

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 19, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A flaw in Broadcom’s Wi-Fi setup software lets an attacker within radio range run code as root on Broadcom-based routers, without the network password or any pairing step, security researcher Quentin Kaiser disclosed on October 16.

    He showed the attack working against home gateways supplied by three Belgian internet providers, in one case reading the Wi-Fi password off the device and in another opening a remote shell over the air. No CVE has been assigned to the flaw, and no fix has been deployed to the affected routers, Kaiser says.

    The flaw is in Broadcom’s version of Wi-Fi Protected Setup (WPS), the feature that lets a device join a Wi-Fi network without the password being typed in. Broadcom’s code mishandles the reassembly of fragmented WPS setup messages, so an attacker in range can send crafted messages that corrupt the router’s memory. From there, Kaiser built two things: a way to read memory back off the device, and a way to run his own code on it.

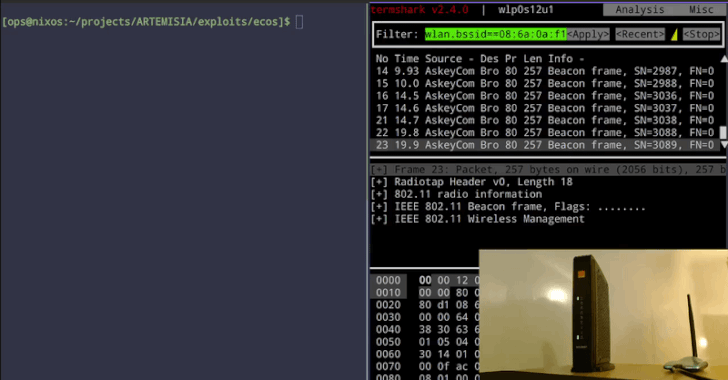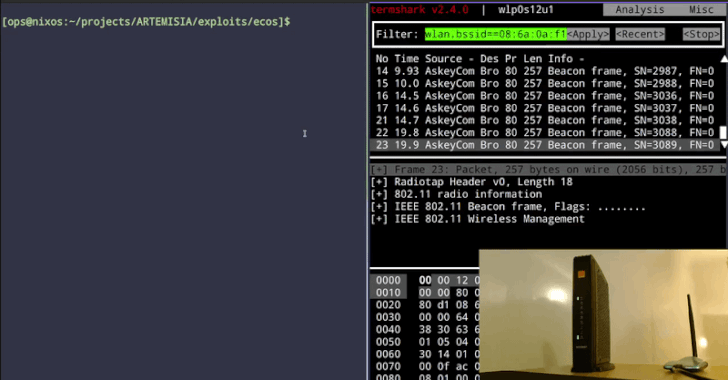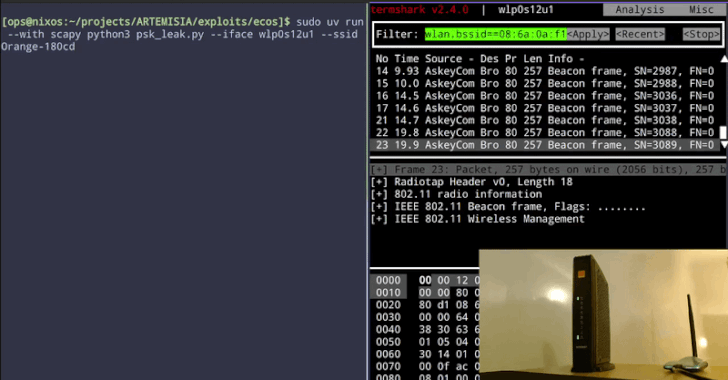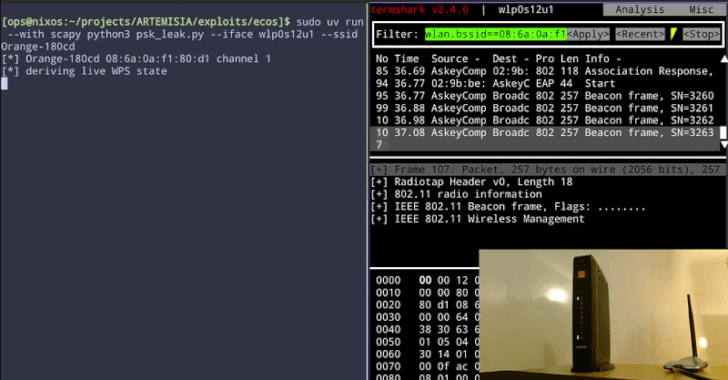
    Against an Orange Belgium gateway, the Askey TCG3000 read the Wi-Fi password (the PSK) from the router’s stored settings, sent it back over the air, and then joined the network with it.

    Against a Proximus gateway, the Sagemcom-built BBOX3V+, the exploit opened a reverse shell, a remote command line, carried over Wi-Fi frames, so no outside server was needed.

    Cybersecurity

    Both ran without any login, and the attack works at a distance, not only up close, Kaiser says. He reports no real-world attacks using the flaw. The working exploits are his own.

    What’s Affected

    Broadcom’s WPS code is embedded in routers and access points from dozens of vendors, and Kaiser estimates that millions of devices worldwide are affected.

    The vulnerable chips fall into two families: older eCos-based models (the BCM3380, BCM3383 and BCM33834), where he found no usable fix and calls the bug a permanent “forever day,” meaning a flaw that will never be patched on those devices, and newer Linux-based models (the BCM3390, BCM65xx and BCM68xx), which could be fixed if their makers switch Wi-Fi software.

    In Belgium, Kaiser found the flaw present and exploitable on gateways from three of the four big providers: Proximus, Orange Belgium and VOO. A fourth, Telenet, may be affected too, but he could not test one.

    A wider list he published, ranging from Cisco small-business access points to Huawei and ARRIS routers, mixes confirmed and unconfirmed entries, and some rest on an automated check that only flags a device as “likely vulnerable.”

    The Belgian per-provider counts, he says, run into the hundreds of thousands of gateways, but are rough estimates.

    Why There’s No Patch, and No CVE

    The flaw is old. Kaiser traces the code back to at least 2010 and says Broadcom shipped an incomplete fix in 2018, then told customers to switch to a different Wi-Fi software package, called hostapd, rather than relying on the fix. On the older eCos chips, he says, no working fix was ever shipped, which is why he calls it a forever day.

    No CVE, the tracking identifier that lets defenders and vendors follow a flaw, has been assigned to it. Kaiser says Broadcom told him it has known about the bug since 2018 and had heard about it from others, but would not register a CVE or say anything publicly, which he believes is why so many device makers never patched.

    Cybersecurity

    When he took the case to the CERT Coordination Center, it was closed the same day, because Broadcom itself holds the authority to assign CVEs for its products and would not do so. The Hacker News found no CVE for the flaw as of October 19.

    What Defenders Can Do

    There is no patch to install, and no setting Kaiser points to that blocks the attack over the air. What he provides instead is a way to find affected gear: YARA rules that spot the vulnerable code in extracted firmware, and a script that listens to a live access point and reports whether it looks vulnerable.

    Both are triage aids, he notes: a patched device can still match the rules, so a hit is a reason to check further, not a confirmed finding. For gear that will never be fixed, replacement is the practical option.

    Kaiser frames the bug as well suited to attackers who reach a target over nearby Wi-Fi rather than the internet, a technique Russian state hackers have used to breach networks from across the street.

    Attackers Broadcom Code Flaw lets range Root routers Run unpatched WiFi
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Anthropic Acquires Confidential AI Startup Opaque Systems

    Hackers exploit SiteGuard WAF flaw to run commands as SYSTEM, root

    US Cybersecurity Job Postings Fall 26% as AI Security Engineer Demand Soars

    ConnectWise Suspends Cloud Backup After Attackers Compromise Microsoft 365 Tenants

    Why AI Confidence Is Not Validation

    Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Bomb threat forces Tel Aviv to Vienna flight to land in Bulgaria

    October 19, 2026

    Burnham pledges ‘big changes’ to the way the welfare system works to tackle Neets crisis – UK politics live | Politics

    October 19, 2026

    From climate and nature risks to economic resilience and competitiveness

    October 19, 2026

    Anthropic Acquires Confidential AI Startup Opaque Systems

    October 19, 2026
    Latest Posts

    Adobe Patches Three CVSS 10.0 ColdFusion and Campaign Classic Flaws

    August 13, 2026

    Google’s Pixel 11 phone preorders come with up to $350 in gift cards

    August 13, 2026

    Hong’s Defeat in Wisconsin Sparks New Disagreements Within Democratic Party

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Bomb threat forces Tel Aviv to Vienna flight to land in Bulgaria

    October 19, 2026

    Burnham pledges ‘big changes’ to the way the welfare system works to tackle Neets crisis – UK politics live | Politics

    October 19, 2026

    From climate and nature risks to economic resilience and competitiveness

    October 19, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.