

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Just as Saint Nige thought it was safe to reappear, along comes pesky ITV | John Crace

    October 15, 2026

    Steam can now show game achievements in separate ‘sets’

    October 15, 2026

    Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory

    October 15, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Just as Saint Nige thought it was safe to reappear, along comes pesky ITV | John Crace
    • Steam can now show game achievements in separate ‘sets’
    • Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory
    • Scammer Loses $4.8M Stored On Tampered Ledgers: Asia Express
    • A telling hole in a Neandertal bone hints at a bitter end
    • Heavy rain shuts down Istanbul, causing flooding and 3 deaths
    • Starlink’s Ukraine and India Fights Test Elon Musk’s Power
    • Fake image depicting real attack on protester at Trump rally spreads online
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, October 15
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Hackers exploit Collabora RCE flaw to backdoor Nextcloud servers

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 15, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Threat actors are exploiting a critical command execution flaw, now tracked as CVE-2026-110447, in the Collabora Online – Built-in CODE Server app (richdocumentscode) for Nextcloud.

    Multiple administrator reports indicate that attacks began in mid-September, roughly a month before the formal security bulletin, the GitHub advisory, and CVE publication.

    CVE-2026-110447 impacts richdocumentscode versions before 26.4.303 and resides in the Nextcloud app’s mechanism for starting the bundled Collabora server.

    The flaw affects only the optional built-in CODE server app. Standalone Collabora Online servers, Docker and RPM/DEB installations, and Nextcloud All-in-One deployments remain unaffected, according to Collabora.

    The attacks involve sending a malicious request to the app’s proxy.php endpoint, triggering OS command injection.

    A key prerequisite for successful exploitation is that the built-in CODE server must be stopped (e.g., after a restart, upgrade, crash). Authentication or user interaction is not required.

    System administrators impacted by malicious activity reported attacks against multiple endpoints dating back to September 10.

    According to the reports, the attacker planted PHP webshells and used them to search for password databases, password manager artifacts, and cryptocurrency wallets.

    Some users also reported that ransomware operators are exploiting the flaw, but BleepingComputer could not independently confirm this.

    System administrators are recommended to upgrade to version 26.4.303 or later, or remove the server app if not needed. The vendor warned that disabling the app is insufficient.

    Beyond the mid-September warnings from maintainers, a community warning was also published on October 3, urging administrators to update immediately due to ongoing exploitation.

    However, the lack of a CVE ID made it more difficult for administrators to pinpoint the issue correctly and implement efficient defenses.

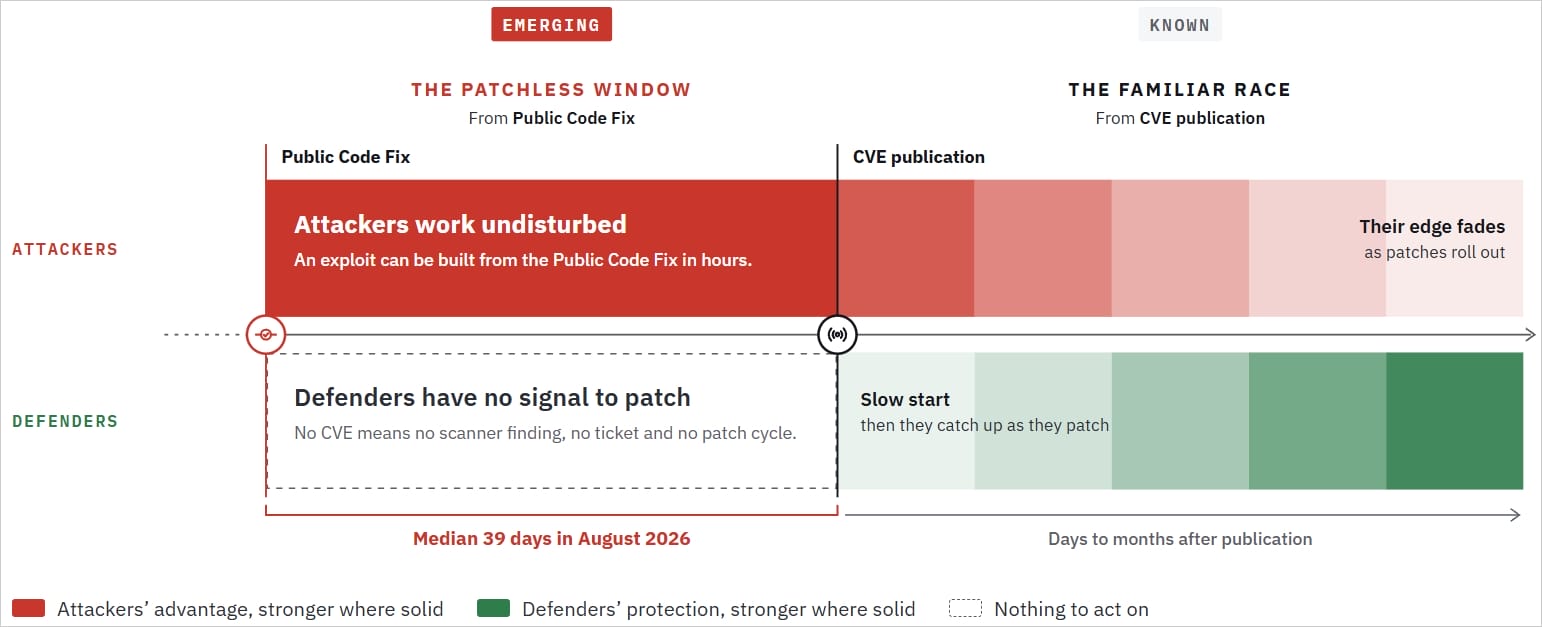
    A study from cybersecurity company Second Security illustrates the gap between security fixes and formal vulnerability notifications.

    The firm analyzed real-world examples from open-source flaws and found that the median interval between public fixes and CVE publication was 39 days in August, up from 5.1 days in January.

    The researchers suggest that growing volumes of AI-assisted vulnerability discoveries are straining CVE processing and contributing to publication delays.
    Diagram
    Source: Second Security

    In many cases, the researchers found public exploit code emerged online within hours of a security fix and several days before the corresponding CVE was published.

    Second Security notes that the use of AI tools makes it easy for attackers to generate working exploits for published fixes.
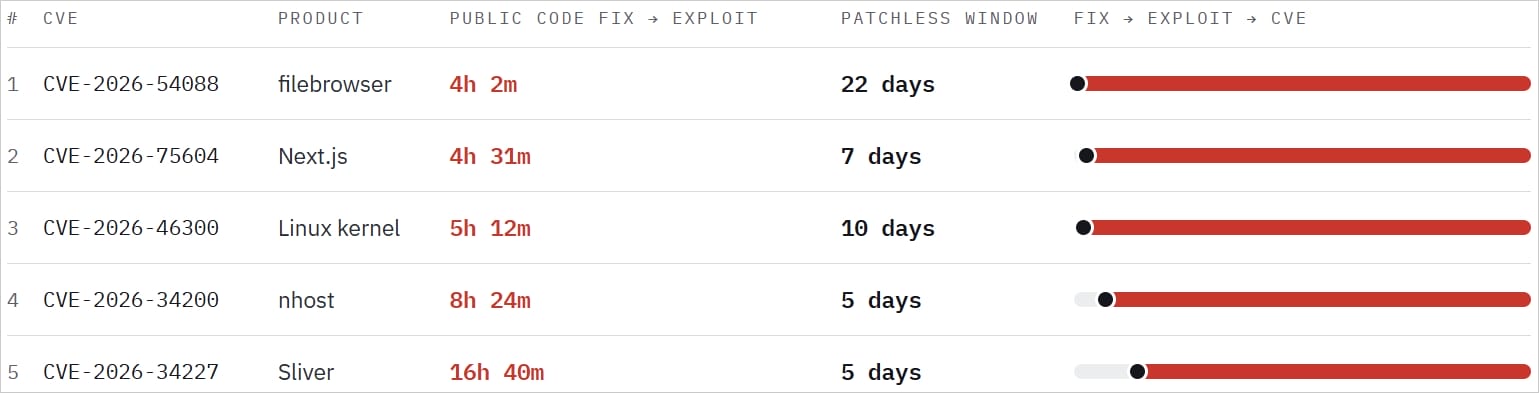
    Examples of PoC and CVE appearance times
    Examples of public exploits and CVE appearance times
    Source: Second Security

    In Collabora’s case, the fix was committed on September 9, and version 26.4.303 was released on September 11. The advisory and CVE were published on October 14, a gap of more than four weeks.

    BleepingComputer contacted Nextcloud with questions about its response to the malicious activity reports, as well as details about the attacks and the number of impacted systems.

    Nextcloud told BleepingComputer that Collabora reported the vulnerability in mid-September and that an update became available through the app store.

    The company justified the disclosure delay by saying it gave users time to update and that it had not observed widespread exploitation.

    In a blog post earlier today about the activity, Collabora attributed the delayed announcement primarily to GitHub CVE-processing backlogs, which it said were under strain from increasing volumes of AI-driven security reports.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    Backdoor Collabora exploit Flaw hackers Nextcloud RCE Servers
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory

    Ransomware extortion gets personal as attackers target employees’ families

    Context Is King in the Fight Against Modern Cyberattacks

    ThreatsDay: Adobe RCE, DNS Wallet Theft, NVIDIA Container Escape, Self-Healing Backdoor + 23 More

    Fake Arch Linux packages push malware with root privileges

    UK Legal Aid Agency Hack Scope Widens After Forensic Review

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Just as Saint Nige thought it was safe to reappear, along comes pesky ITV | John Crace

    October 15, 2026

    Steam can now show game achievements in separate ‘sets’

    October 15, 2026

    Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory

    October 15, 2026

    Scammer Loses $4.8M Stored On Tampered Ledgers: Asia Express

    October 15, 2026
    Latest Posts

    Early release scheme risks more serious crimes, probation chief warns

    August 12, 2026

    UK heatwave live: Met Office issues extreme heat warning as government convenes emergency Cobra meeting | Extreme heat

    August 12, 2026

    Rybakina defeats Osaka, advances to Canadian Open semifinals to play Gauff | Tennis News

    August 12, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Just as Saint Nige thought it was safe to reappear, along comes pesky ITV | John Crace

    October 15, 2026

    Steam can now show game achievements in separate ‘sets’

    October 15, 2026

    Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory

    October 15, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.