


The FBI has seized seven domains used by Chinese state-sponsored hackers known as Flax Typhoon to operate two hacking tools, MicroScan and FishHub, used in attacks that breached critical infrastructure and other organizations worldwide.
The seizures targeted infrastructure supporting the two hacking platforms allegedly operated by China-based Integrity Technology Group (Integrity Tech), which U.S. authorities say has contracts with the Chinese government.
According to the U.S. Department of Justice, the tools were used to scan for vulnerabilities and breach critical infrastructure networks in the United States and other countries.
“Integrity Technology Group provided China-linked threat actors with capabilities used to conduct widespread vulnerability scanning and, in some cases, intrusions targeting U.S. and foreign critical infrastructure,” said Brett Leatherman, assistant director of the FBI’s Cyber Division.
Leatherman said the Chinese government relies on contractors and other companies to expand the reach of their cyber operations, and that disrupting these organizations makes it harder for China-linked hackers to target American networks.
MicroScan is a vulnerability-scanning platform developed by Integrity Tech to identify security weaknesses in targeted networks.
According to an FBI seizure affidavit, the platform was used along with a botnet of internet-connected devices infected with Mirai malware to scan potential targets.
These targets include a South Carolina power company, airports in Japan and Poland, Taiwanese natural gas and electricity companies, and universities.
The affidavit also confirms that the scanning activity led to successful breaches, including at two Taiwanese universities whose networks were scanned using MicroScan in August 2022 and March 2023 and subsequently breached.
While the FBI confirmed that the hacking tools were used in intrusions involving critical infrastructure, it did not disclose whether the specifically named power companies, airports, and energy providers were successfully breached.
The FBI seized the c0cc.cc domain used by Integrity Tech to access the MicroScan platform, which law enforcement confirmed was online in September 2026.
The second platform, FishHub, was used to conduct spear-phishing attacks and deliver additional malware to networks already compromised.
The malware gave attackers unauthorized remote access to victims’ networks and allowed them to search for specific files and exfiltrate data to servers controlled by Integrity Tech.
According to the FBI seizure affidavit, investigators found data and files belonging to more than 20 organizations on a server linked to the FishHub data-theft tool, including six universities in Taiwan.
Law enforcement seized five domains used to deliver the malware: 98aicai.com, 98aicode.com, outlook3650.com, youtubecard.com, and linkedinns.net.
A seventh seized domain, 98aiblog.com, was tied to the SoftEther VPN software installed on compromised systems to maintain remote access to victim networks.
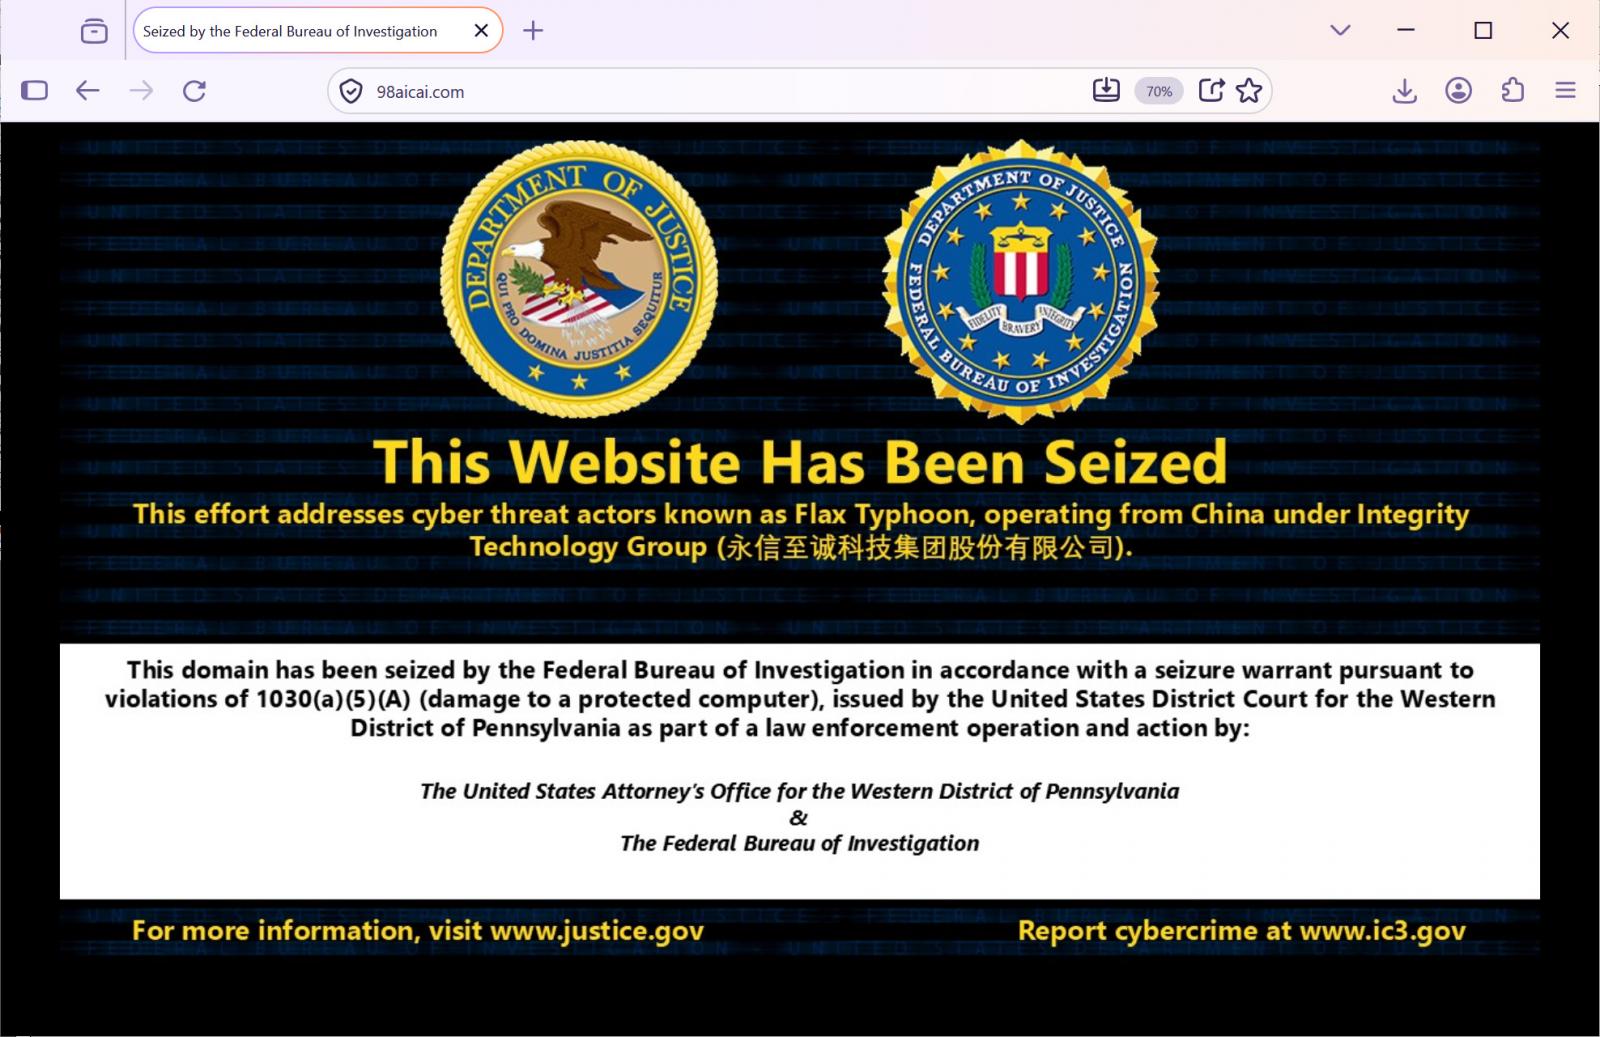
The seized domains now display FBI seizure notices identifying the Flax Typhoon hacking group and Integrity Technology Group.
Source: BleepingComputer
In coordination with the domain seizures, the FBI, CISA, NSA, and international partners issued a joint cybersecurity advisory explaining how Chinese government-linked hackers used Integrity Tech’s tools and infrastructure to compromise organizations and steal sensitive information.
The advisory says the attackers targeted U.S. government agencies, critical manufacturing, healthcare, information technology, law enforcement, educational institutions, and religious organizations, as well as organizations in Southeast Asia, Africa, and North America.
The activity overlaps with operations tracked as Flax Typhoon, Ethereal Panda, and Red Juliett, although the agencies say that not all activity may necessarily be linked to Integrity Tech.
According to the advisory, MicroScan is a Python-based vulnerability scanner containing more than 1,300 penetration-testing scripts used to identify security flaws in websites and services.
These scripts targeted widely used software, including Oracle WebLogic, Apache Struts, WordPress, Jenkins, and other applications.
Investigators also identified eight vulnerabilities that were commonly targeted by the hackers:
- CVE-2015-3306: ProFTPD unauthorized file read vulnerability.
- CVE-2015-5477: ISC BIND denial-of-service vulnerability.
- CVE-2016-3081: Apache Struts remote code execution vulnerability.
- CVE-2021-3199: ONLYOFFICE DocumentServer unauthorized file write vulnerability.
- CVE-2023-22894: Strapi information disclosure vulnerability.
- CVE-2014-6278: GNU Bash (Shellshock) remote code execution vulnerability.
- CVE-2019-11510: Pulse Secure VPN arbitrary file read vulnerability.
- CVE-2021-22205: GitLab remote code execution vulnerability.
The attackers also used the open-source EBurst tool to conduct password-spraying attacks against Microsoft Exchange servers, along with other tools to steal emails, collect Active Directory credentials, and exfiltrate data.
The FBI also discovered a custom web application that let third parties browse stolen emails without needing direct access to the compromised accounts.
The joint advisory contains indicators of compromise, including IP addresses, domains, malware hashes, and details of the attackers’ tools, to help organizations identify potential intrusions.
Authorities are urging organizations to review the indicators, patch vulnerable systems, disable unnecessary exposed services, and enforce multifactor authentication to protect against attacks.
This is not the first time US law enforcement disrupted Integrity Tech’s hacking infrastructure.
In September 2024, the Justice Department disrupted an Integrity Tech-operated Mirai botnet consisting of more than 200,000 compromised consumer devices worldwide.
The UK government also sanctioned Integrity Tech in 2025, and the European Union sanctioned the company in 2026 for involvement in cyberattacks targeting Europe and its allies.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
