

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Did Trump say planes will have to ‘fly a little bit slower’?

    November 20, 2026

    Ukraine: Three Kyiv bridges hit during major Russian missile attack

    November 20, 2026

    UK government borrowing rises less than forecast in surprise boost for chancellor John Healey | Government borrowing

    November 20, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Did Trump say planes will have to ‘fly a little bit slower’?
    • Ukraine: Three Kyiv bridges hit during major Russian missile attack
    • UK government borrowing rises less than forecast in surprise boost for chancellor John Healey | Government borrowing
    • What Trump, Putin and Xi Left on the Table
    • The Stormy Southwest Pacific   – NASA Science
    • Doctors’ strike: Warning staff will leave NI for better pay
    • One in four land reptiles depends on rock habitats. Lack of protection leaves them in a hard place
    • Ohio Program Wants $1M Back After Company Fails to Deliver GMO Salmon — ProPublica
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Friday, November 20
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Citrix NetScaler Post-Exploitation Payload Creates Superuser, Maps Web Shell to CSS-Like URLs

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 3, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananOct 01, 2026Vulnerability / Web Security

    Threat actors have been observed exploiting a critical pre-authentication command injection vulnerability in Citrix NetScaler ADC and NetScaler Gateway to drop web shells and attempt theft of configuration data.

    LevelBlue’s Threat Hunt Operations & Research (THOR) team, which analyzed the exploitation activity across multiple customer environments, said it identified malicious NetScaler authentication events containing attacker-controlled usernames designed to weaponize CVE-2026-88771.

    CVE-2026-88771 (CVSS score: 9.5) is an improper input validation vulnerability that could allow an unauthenticated attacker to execute arbitrary commands.

    The security flaw, along with CVE-2026-88772, was disclosed last week after reports that the Dutch National Cyber Security Centre (NCSC-NL) reportedly sent a pre-notification to organizations in the Netherlands that urged organizations to shut their appliances down, citing active exploitation. As of writing, there are currently no details about who is behind these efforts.

    Cybersecurity

    “One of the most consistent characteristics across the identified events was attacker-controlled authentication data containing variations of the pitboss and NSPPE strings associated with exploitation of CVE-2026-88771,” LevelBlue said.

    Other attempts have been observed using curl or wget to fetch additional payloads from external servers, or extract NetScaler configuration data –

    • 64.94.85[.]67:443/update_c08937.pl
    • 31.56.197[.]72:9090/lula
    • 23.27.143[.]20:9000/main.py

    “Taken together, the observed commands demonstrate activity extending beyond basic vulnerability validation,” LevelBlue said. “The attempts included payload retrieval and execution as well as collection and staging of NetScaler configuration data.”

    Notable among the second-stage payloads is a Python script (“main.py”) that’s designed to establish a reverse shell to “45.141.21[.]130” over TCP port 443. It also searches for running processes associated with “/var/python/bin/customsnmpd” and forcefully terminates them by issuing a “kill -9” command.

    Another second-stage payload, “update_c08937.pl,” is a Perl script with several post-exploitation capabilities –

    • Modify “/flash/nsconfig/ns.conf” to create a local account named sec_monitor and assign it the superuser role.
    • Archive the “/flash/nsconfig” directory into “/tmp/update_result_3567cs.tgz” and upload the resulting archive containing NetScaler configuration data to “64.94.85[.]67:443.” The script then deletes the archive and erases itself to reduce the forensic footprint on disk.
    • Change the permissions of “/bin/sh” to 6555 and deploy a PHP web shell at “/var/netscaler/logon/LogonPoint/.local_journal” for remote command execution and file upload and download.
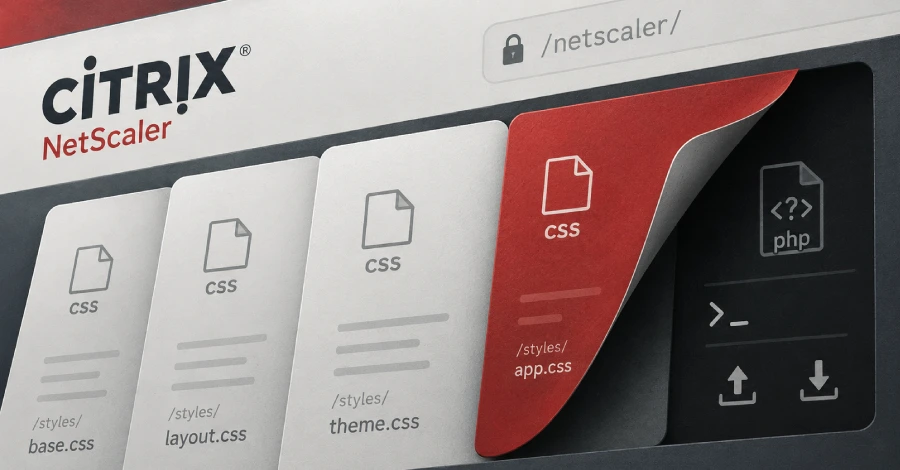
    • Modify “/etc/httpd.conf” to enable PHP execution and map the web shell to URLs resembling legitimate NetScaler CSS resources, corroborating activity observed by GreyNoise.
    Cybersecurity

    “While some attempts used commands such as whoami to test command execution, others attempted to retrieve additional payloads, collect NetScaler configuration data, establish reverse shells, create privileged accounts, and deploy web shells,” LevelBlue said.

    The disclosure comes a day after Mandiant Consulting and Google Threat Intelligence Group (GTIG) said dozens of organizations have been impacted by attacks exploiting CVE-2026-88772 to deliver PHP web shells, like WHIPSHOT, and a Python tunneler dubbed SLAPSHOT.

    Citrix creates CSSLike Maps NetScaler Payload PostExploitation Shell Superuser URLs Web
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Study maps jaguars across the Americas to help their populations rebound

    Ordnance Survey maps go the extra mile | Ordnance Survey

    0sec Labs Open-Sources 0, an AI Security Harness With Web UI, CLI and MCP

    The Guardian view on Ordnance Survey maps: still a superior way to navigate the landscape | Editorial

    Did Apple Maps replace satellite imagery of Gaza destruction with old photos? What we know

    How Online Maps Lay Bare the US Military Bases Targeted by Iran

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Did Trump say planes will have to ‘fly a little bit slower’?

    November 20, 2026

    Ukraine: Three Kyiv bridges hit during major Russian missile attack

    November 20, 2026

    UK government borrowing rises less than forecast in surprise boost for chancellor John Healey | Government borrowing

    November 20, 2026

    What Trump, Putin and Xi Left on the Table

    November 20, 2026
    Latest Posts

    China joins Europe in scrapping Windows for Linux

    August 21, 2026

    We would like to speak to people who have been homeless in England about what helped them off the streets | Homelessness

    August 21, 2026

    Tracking UK migration: Small boats, asylum hotels and visas

    August 21, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Did Trump say planes will have to ‘fly a little bit slower’?

    November 20, 2026

    Ukraine: Three Kyiv bridges hit during major Russian missile attack

    November 20, 2026

    UK government borrowing rises less than forecast in surprise boost for chancellor John Healey | Government borrowing

    November 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.