

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Why Trader Joe’s ‘Everything but the Bagel’ seasoning is banned in South Korea

    November 19, 2026

    Why depth beats breadth in Europe’s hunt for an AI edge – POLITICO

    November 19, 2026

    New law ‘may be needed’ after Google rejects call to remove Russell Brand’s YouTube prison message | Russell Brand

    November 19, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Why Trader Joe’s ‘Everything but the Bagel’ seasoning is banned in South Korea
    • Why depth beats breadth in Europe’s hunt for an AI edge – POLITICO
    • New law ‘may be needed’ after Google rejects call to remove Russell Brand’s YouTube prison message | Russell Brand
    • NASA Data Clinches First-of-Its-Kind Stellar Merger
    • Skinks in boots: How Hong Kong emerges as key hub in Australia’s native reptile trafficking
    • AlloySelect relaunches at Offshore Energy 2026 with new CCS screening preview
    • This year, the Greens have reshaped British politics. Now we need party systems to match that influence | Caroline Lucas
    • Old warning about alleged Christmas postal ‘scam’ reshared online – Full Fact
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, November 19
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 25, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananSep 25, 2026Malware / Supply Chain Attack

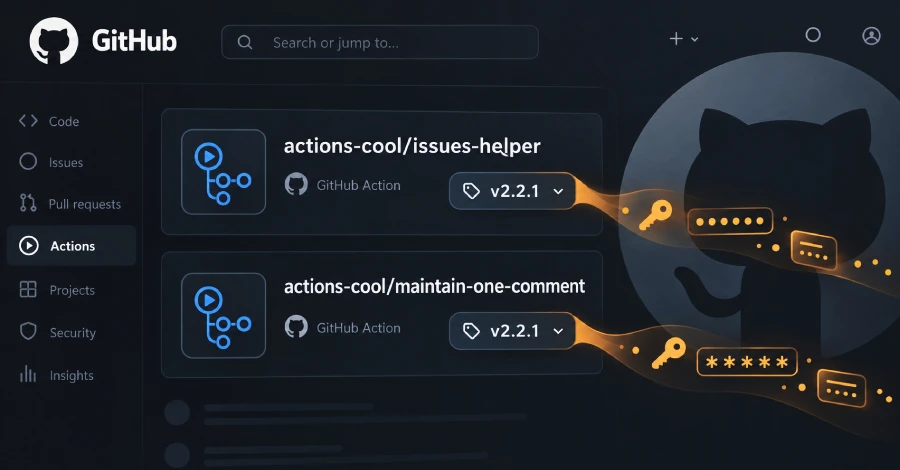
    Two actions-cool GitHub Actions have been disabled for a second time after the repositories became accessible last week, months after they were compromised during the May 2026 Mini Shai-Hulud campaign.

    The affected GitHub Actions are listed below –

    Visiting either of the repositories now shows the message: “Access to this repository has been disabled by GitHub Staff due to a violation of GitHub’s terms of service. If you are the owner of the repository, you may reach out to GitHub Support for more information.”

    “On September 16, 2026, both repositories became accessible again,” Socket researcher Karlo Zanki said. “Their release tags were not cleaned up first. They still point to the malicious content introduced on May 18, so any workflow that references either action by a version tag resumed downloading and executing the payload on its next run.”

    Cybersecurity

    The two GitHub Actions workflows were originally compromised on May 18, 2026, to run malicious code that harvested sensitive credentials from CI/CD pipelines that ran them and exfiltrated the details to an attacker-controlled server.

    The activity was subsequently linked to the Mini Shai-Hulud activity cluster, citing overlaps in the exfiltration domain (“t.m-kosche[.]com”) used in the GitHub Actions workflows and the npm packages from the @antv ecosystem.

    “That points to the same Mini Shai-Hulud activity cluster, not a separate npm-only incident,” Philipp Burckhardt, head of threat intelligence at Socket, told The Hacker News at the time.

    The repositories were re-enabled on September 16, 2026, at some point between 11:09 a.m. and 6:16 p.m. GMT+2. It’s currently not known why this occurred.

    But the latest development points to another problem: the malicious code remained in the affected codebases and never cleaned up, and all that was required to activate the threat was for the repositories to become downloadable again.

    Given that there are still several workflows that use the two GitHub Actions, the exposure could have led to severe software supply chain security risks without the need for the threat actors to use a new exploit or set up new infrastructure.

    “Both actions automate issue and comment housekeeping, such as closing inactive issues, checking newly opened ones, or keeping a single bot comment up to date,” Socket said.

    “The workflows that call them usually run on a daily schedule or whenever someone opens an issue or pull request. In practice, most affected repositories probably ran the payload within a day of the re-enablement, with no further action needed from the threat actor.”

    Cybersecurity

    The issue does not impact workflows that pin either action to the full commit SHA of a version from before May 18, 2026. Developers are recommended to carry out the following steps –

    • Locate every reference to the affected actions and treat “actions-cool/issues-helper@v2.2.1” as affected.
    • Remove the actions and pin them to a known-clean SHA that predates May 18, 2026.
    • Rotate all exposed secrets.
    • Review workflow run history and check for newly successful runs after a prolonged period of Set up job failures.
    • Audit repository history for unexpected commits after September 16, 2026.

    “Most supply chain incidents involve something new: a newly published malicious version, a newly hijacked account, or a newly injected workflow,” Zanki said. “This one did not. No new code was published and no configuration was changed.”

    “This incident shows that a mutable tag can be compromised, contained, and then reactivated without any change to your own workflow file. SHA pinning removes that dependency on the upstream repository’s state.”

    Actions Compromised Executing GitHub Malware mini online resumed ShaiHulud
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Old warning about alleged Christmas postal ‘scam’ reshared online – Full Fact

    Fake National Grid warning about ‘major blackout’ shared online – Full Fact

    Home Office accused of trying to cancel online talk by Andreas Malm | Home Office

    AI-generated video of England flag hung on building works shared online – Full Fact

    Brussels takes on the evils of online commerce – POLITICO

    Fake images of Donald Trump being carried after US midterm elections shared online – Full Fact

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Why Trader Joe’s ‘Everything but the Bagel’ seasoning is banned in South Korea

    November 19, 2026

    Why depth beats breadth in Europe’s hunt for an AI edge – POLITICO

    November 19, 2026

    New law ‘may be needed’ after Google rejects call to remove Russell Brand’s YouTube prison message | Russell Brand

    November 19, 2026

    NASA Data Clinches First-of-Its-Kind Stellar Merger

    November 19, 2026
    Latest Posts

    After one week wearing the Pixel Watch 5, here’s what I want most

    August 21, 2026

    Targeted by an Islamophobic Provocateur, a City’s Muslims Are on Edge

    August 21, 2026

    Back on track: can Burnham fix the north’s woeful rail services? | Rail industry

    August 21, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Why Trader Joe’s ‘Everything but the Bagel’ seasoning is banned in South Korea

    November 19, 2026

    Why depth beats breadth in Europe’s hunt for an AI edge – POLITICO

    November 19, 2026

    New law ‘may be needed’ after Google rejects call to remove Russell Brand’s YouTube prison message | Russell Brand

    November 19, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.