

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Marvell, Microsoft & Oracle Work to Standardize Data Centers

    October 21, 2026

    Astronauts’ hearts just passed a surprising test for Mars

    October 21, 2026

    Extractive industries threaten global goal to protect 30% of nature by 2030, report finds

    October 21, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Marvell, Microsoft & Oracle Work to Standardize Data Centers
    • Astronauts’ hearts just passed a surprising test for Mars
    • Extractive industries threaten global goal to protect 30% of nature by 2030, report finds
    • A plan to ensure energy is affordable for all | Energy bills
    • Jeffrey Donaldson investigated over alleged rape in UK parliament | Northern Ireland
    • Gas go-ahead ignites oily response from Trump, while speaker seems ready to blow | John Crace
    • Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
    • Tracks Along the Longest Drive on Another World
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Wednesday, October 21
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Critical Elementor Pro flaw exploited to take over WordPress sites

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 4, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A recently patched critical vulnerability (CVE-2026-32475) in the Elementor Pro plugin for WordPress is being exploited in attacks that deliver a webshell payload and execute arbitrary commands on the server.

    Elementor Pro is a popular WordPress plugin with more than 6 million active installations, allowing users to build websites using a drag-and-drop interface.

    The CVE-2026-32475 vulnerability was patched on August 19. Since then, Defiant’s Wordfence web application firewall has blocked almost 200,000 exploitation attempts targeting its clients.

    The issue stems from faulty validation of file-upload arrays in Elementor Pro forms and is present in versions 4.2.1 and earlier.

    By submitting an empty file as the first array element and a malicious PHP file as the second, attackers can cause the plugin to stop validating subsequent files.

    The uploaded payload is stored under /wp-content/uploads/elementor/forms/ and can then be accessed to execute commands remotely.

    WordPress cybersecurity platform Patchstack warned last month that attackers could exploit it to upload arbitrary PHP files and trigger PHP code execution on the server.

    Exploitation is only possible when a site has a published Elementor Pro Form widget containing at least one File Upload field, a common configuration.

    Yesterday, Wordfence alerted that activity exploiting CVE-2026-32475 started on August 19, the same day Elementor released version 4.2.2 that addressed the vulnerability.

    “The attacker submits the form’s File Upload field as an array, where the first element is empty and the second element carries a PHP payload with a .php filename, which is the structure that triggers the validation bypass,” Wordfence says.
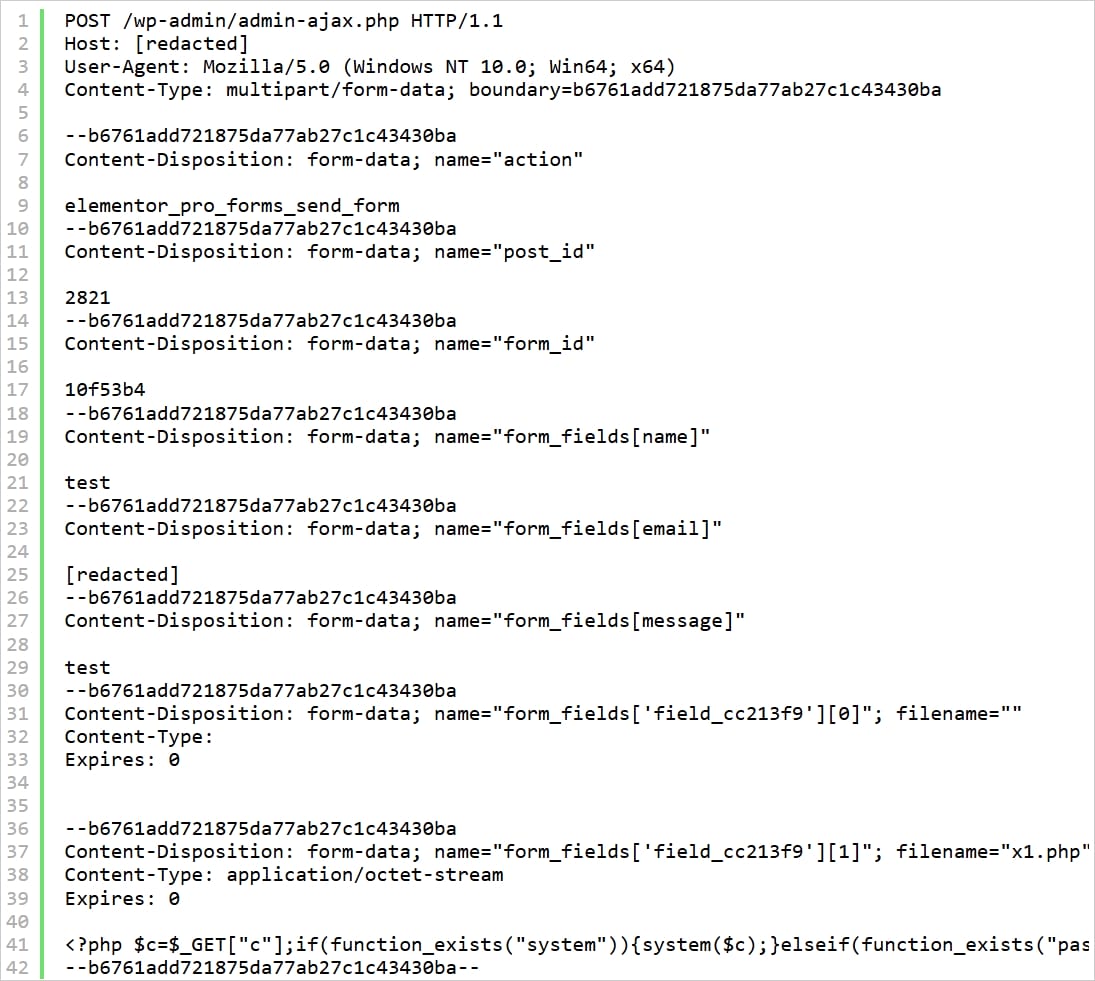
    Example malicious request
    Example malicious request
    Source: Wordfence

    “Once written, the uploaded PHP file is placed in the /wp-content/uploads/elementor/forms/ directory under a randomly generated filename with the attacker-supplied .php extension, and the attacker can request it directly to execute arbitrary commands on the server,” the security firm notes.

    Wordfence observed increased attack activity between August 19 and 23, reporting more than190,000 blocked exploitation attempts.

    A list of IP addresses that launched thousands of attacks is also provided so that defenders can add them to their blocklists.

    Administrators should upgrade to Elementor Pro 4.2.2 or later immediately and inspect the /wp-content/uploads/elementor/forms/ directory for rogue PHP files.

    Since this location is used to store uploaded form submissions, the presence of a PHP file is a strong indicator of compromise that should trigger clean-up operations.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    critical Elementor Exploited Flaw Pro sites WordPress
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Marvell, Microsoft & Oracle Work to Standardize Data Centers

    Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases

    CISA: Hackers chain Plex flaws in Plex2Shell attacks to breach servers

    Google Hardens Chrome Against ClickFix Attacks, Insecure HTTP Connections

    Optiv Launches CyberBOT Cybersecurity Awareness Training Program

    PHP Issues Emergency Patches for Two Critical PHP2Shell RCE Flaws as Exploit Attempts Emerge

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Marvell, Microsoft & Oracle Work to Standardize Data Centers

    October 21, 2026

    Astronauts’ hearts just passed a surprising test for Mars

    October 21, 2026

    Extractive industries threaten global goal to protect 30% of nature by 2030, report finds

    October 21, 2026

    A plan to ensure energy is affordable for all | Energy bills

    October 21, 2026
    Latest Posts

    Leavitt to depart the White House

    August 13, 2026

    Israeli troops force families from homes amid settler terror campaign in West Bank | West Bank

    August 13, 2026

    Video of children being taught Muslim prayers does not show a school in England – Full Fact

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Marvell, Microsoft & Oracle Work to Standardize Data Centers

    October 21, 2026

    Astronauts’ hearts just passed a surprising test for Mars

    October 21, 2026

    Extractive industries threaten global goal to protect 30% of nature by 2030, report finds

    October 21, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.