

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    USPS Delays Are Driving Up Ballot Rejections — ProPublica

    October 22, 2026

    A violent and coordinated youth uprising? That’s exactly the picture Europe’s enemies want to paint | Alberto Alemanno

    October 22, 2026

    Does video show 2026 ‘No Kings’ rallies in 7 US cities?

    October 22, 2026
    Facebook X (Twitter) Instagram
    Trending
    • USPS Delays Are Driving Up Ballot Rejections — ProPublica
    • A violent and coordinated youth uprising? That’s exactly the picture Europe’s enemies want to paint | Alberto Alemanno
    • Does video show 2026 ‘No Kings’ rallies in 7 US cities?
    • Macron accuses foreign leaders of exploiting French riots for political gain
    • MI5 spied on NHS founder Nye Bevan for more than 20 years
    • NVIDIA Nsight Python Tutorial: How to Profile GPU Kernels
    • LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release
    • Scientists find 10 different diets linked to slower aging
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, October 22
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    TerminalFix Uses Fake Cloudflare CAPTCHAs to Deploy Reverse-Tunnel Backdoor

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 30, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananAug 30, 2026Social Engineering / Malware

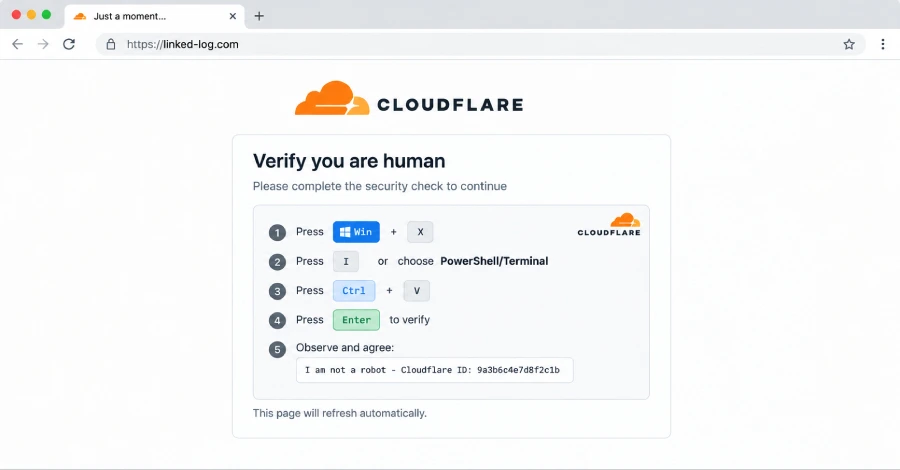
    Microsoft has disclosed details of a new ClickFix variant, dubbed TerminalFix, that aims to trick users into running a malicious command in Windows Terminal or PowerShell.

    “While traditional ClickFix campaigns direct victims to the Windows Run dialog, TerminalFix campaigns apply the same technique but direct users to Windows Terminal or PowerShell instead, increasing the likelihood that complex, multi-line scripts execute successfully,” Microsoft security researchers Sagar Patil, Suriyaraj Natarajan, and Parasharan Raghavan said in an analysis published this week.

    The campaign, targeting organizations across multiple sectors, leverages compromised websites as a starting point to serve fake Cloudflare CAPTCHA verifications that prompt unsuspecting site visitors to copy and execute a malicious PowerShell command.

    The attack chain, per the Windows maker, is a sophisticated multi-stage process that leverages DLL sideloading, steganographic payload extraction, extensive Active Directory reconnaissance, and a bespoke custom reverse-tunnel implant that grants the attacker persistent, network-level proxy access through the infected machine.

    Cybersecurity

    Specifically, the PowerShell command is designed to download a ZIP archive containing a legitimate binary (“LockScreenContentServer.exe”) and a rogue DLL (“dui70.dll”) in order to initiate a DLL sideloading attack.

    The sideloaded DLL is responsible for retrieving next-stage payloads hidden within PNG images from external domains (“bestsocialmedianewspapper[.]com” or “offlineupdater[.]com”), establishes persistence via both Registry Run keys and scheduled tasks, carries out domain reconnaissance, and then deploys a Python-based reverse-tunnel command-and-control (C2) implant.

    The backdoor (“client.py”) is equipped to tunnel arbitrary TCP traffic back to attacker-controlled infrastructure (“gitnow[.]dev:443”) through an encrypted WebSocket channel, as well as enable the C2 server to reach any host visible from the victim’s network.

    The reconnaissance phase involves the following steps –

    • Collect system metadata
    • Perform domain trust discovery, domain admin enumeration, and Active Directory user and computer searches
    • Ping named servers to map the internal network topology

    The attack also delivers a persistent PowerShell file-watch loop that monitors a text file for new commands, executes them via Invoke-Expression, and writes results to an output file.

    Cybersecurity

    “This type of intrusion is particularly dangerous because it provides attackers with direct access to an organization’s internal network through the reverse tunnel,” Microsoft said. “The observed reconnaissance and reverse-tunnel capability could enable an attacker to identify and reach additional systems from a compromised host.”

    The tech giant has warned that such access can be abused further to escalate privileges, disarm security controls, exfiltrate sensitive data, and deploy ransomware, making TerminalFix a serious threat to enterprise environments.

    To mitigate the threat, it’s advised to restrict PowerShell and Run dialog execution for standard users through AppLocker, Application Control for Windows, or Group Policy; consider blocking or auditing the Windows Run dialog (“Win+R”) if it’s not required; monitor for DLL sideloading indicators; train employees to keep an eye out for ClickFix attacks; and enable PowerShell script block logging to detect and analyze obfuscated or encoded commands.

    Backdoor CAPTCHAs Cloudflare Deploy Fake ReverseTunnel TerminalFix
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release

    Authorities disrupt nearly 11,000 cybercrime networks in Africa

    Google Chrome Adds ClickFix Warnings to Stop Users From Running Malicious Commands

    China-Linked Hackers Use ARTEX AI Agents in ConnectWise Supply Chain Attack

    Google Chrome adds Gemini-powered scam detection, warns users of ClickFix attacks

    Memory Bugs Account for Most of Chrome’s 353 New Security Fixes

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    USPS Delays Are Driving Up Ballot Rejections — ProPublica

    October 22, 2026

    A violent and coordinated youth uprising? That’s exactly the picture Europe’s enemies want to paint | Alberto Alemanno

    October 22, 2026

    Does video show 2026 ‘No Kings’ rallies in 7 US cities?

    October 22, 2026

    Macron accuses foreign leaders of exploiting French riots for political gain

    October 22, 2026
    Latest Posts

    Leavitt to depart the White House

    August 13, 2026

    Israeli troops force families from homes amid settler terror campaign in West Bank | West Bank

    August 13, 2026

    Video of children being taught Muslim prayers does not show a school in England – Full Fact

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    USPS Delays Are Driving Up Ballot Rejections — ProPublica

    October 22, 2026

    A violent and coordinated youth uprising? That’s exactly the picture Europe’s enemies want to paint | Alberto Alemanno

    October 22, 2026

    Does video show 2026 ‘No Kings’ rallies in 7 US cities?

    October 22, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.