


Researchers found a way to bypass recent mitigations for Spectre v2 speculative execution side-channel attacks and developed an exploit to leak secrets from Linux machines.
The method works against Spectre v2 defenses on AMD and Intel processors that rely on sanitizing or isolating branch predictors, which researchers generically refer to as neutralization-based mitigations.
Spectre v2 is also known as Branch Target Injection (BTI) and is a variant of the Spectre class of vulnerabilities.
It exploits a processor’s indirect branch predictor and causes it to mispredict the target of an indirect branch, leading to speculative execution along an attacker-influenced code path.
Modern processors use branch prediction to guess the most likely execution path and speculative execution to run instructions along that predicted path before the branch outcome is known.
Spectre v2 allows an attacker to manipulate the CPU’s indirect branch predictor so that the processor speculatively executes instructions at an attacker-chosen location, which could expose sensitive data.
With neutralization-based mitigations (eIBRS on Intel and Safe RET on AMD), there is a gap between the time the branch predictor is isolated and when it is used by the victim branch.
Active Spectre v2 mitigations assume that an attacker cannot use to their advantage the time between cleaning the branch predictor state and using it.
However, the researchers introduced a primitive that enables re-poisoning the CPU’s state after the cleaning but before it is used.
Daniël Trujillo, a PhD student, and associate professor Mengjia Yan of the MIT Computer Science and Artificial Intelligence Laboratory (CSAIL) discovered a technique for exploiting this Time-of-Neutralization to Time-of-Use (TONTOU) window to extract sensitive data.
“An attacker without any special access to read arbitrary memory from the system, including sensitive data such as hashed passwords,” Trujillo told BleepingComputer.
The researchers developed an Interrupt Injection attack, where “unprivileged user programs can schedule timer interrupts to occur during kernel execution.”
“Therefore, we can force the kernel to be redirected to the interrupt handler and use this handler to poison microarchitectural states within the post-neutralization window,” the researchers explain.
The researchers found that interrupts occurring during the post-neutralization window can be used to poison the processor’s indirect branch predictor, enabling attacks against all types of indirect branches.
Mengjia and Trujillo tested the attack starting from the assumption that an attacker can run arbitrary, unprivileged code on a Linux target machine to leak data from the kernel.
On an AMD Zen 2 host with the latest Spectre v2 mitigations, the two researchers successfully ran through all the stages of a TONTOU attack: neutralization, redirection, poisoning, and the use of the poisoned branch predictors.
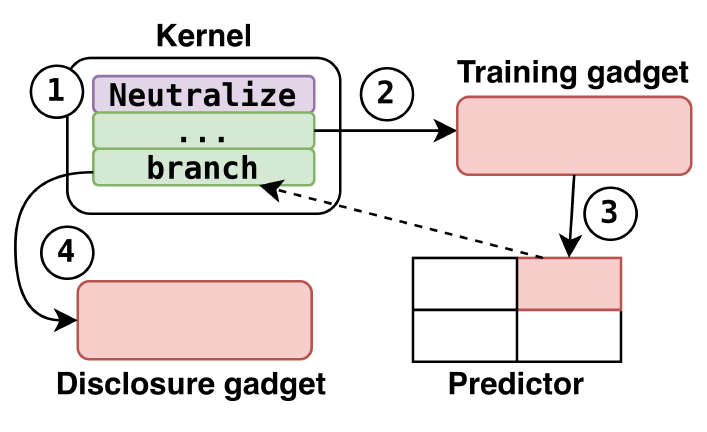
Successfully exploiting the issue requires overcoming several obstacles, including redirecting kernel control flow, precisely aligning interrupts with the post-neutralization window, and using the interrupt handler to poison the branch predictor entry associated with the target indirect branch.
The researchers address these challenges through installing ‘timers’ to trigger hardware interrupts, frequent injection of interrupts, and via active and passive poisoning methods.
The attack was tested on both Intel and AMD processors. On an AMD Zen 2 system running Linux version 6.14.0-37-generic with 16GB of RAM, the researchers showed it could leak arbitrary kernel memory at a rate of 5.47 bytes/s and 91.97% accuracy, including the contents of /etc/shadow, which stores password hashes.
Across 10 test runs, the attack successfully located and extracted the file in five cases, with each attempt taking an average of 18 minutes.
While the attack is also possible on Intel machines, they noted that additional software requirements make the task more complex.
The researchers note that interrupt injection enables attacker-controlled poisoning of the Return Stack Buffer (RSB), causing speculative mispredictions of return targets.
Because passive RSB pollution is less reliable, they combined interrupt injection with Inception, a previously disclosed attack that Daniël Trujillo helped develop.
AMD has published an advisory today noting that the interrupt inject issue “appears to be associated” with how implementation on Linux of the Safe RET mitigation against potential information disclosure attacks.
Daniël Trujillo and Mengjia Yan presented their findings today at the Black Hat USA security conference. They will also share the details at the USENIX Security 2026 between October 27 and 29.

Security teams log 54% of successful attacks and alert on just 14%. The rest move through your environment unseen.
The Picus whitepaper shows how breach and attack simulation tests your SIEM and EDR rules so threats stop slipping by detection.
