


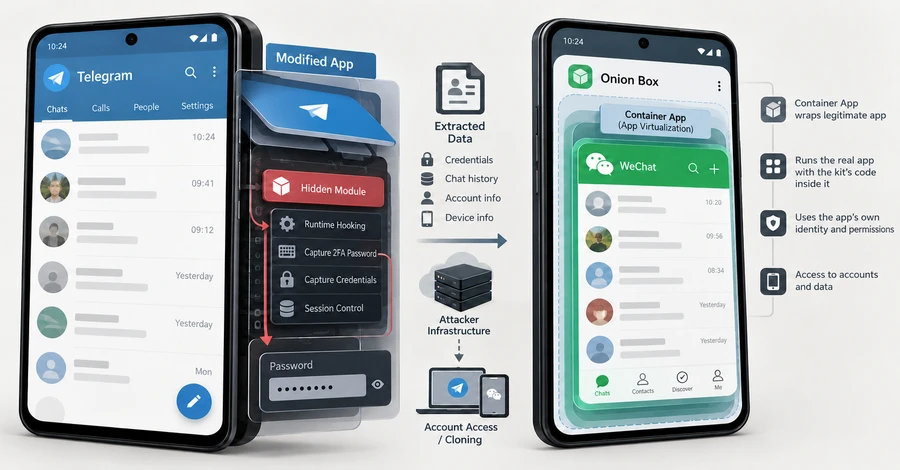
A rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies of the two apps, researcher Ovi found. It only reaches people who install one of these tampered copies, spread outside the official app stores, or who run WeChat inside the kit makers’ own container app.
The kit’s Telegram part matches Baohuo, a backdoor that Doctor Web reported in October 2025. Doctor Web found Baohuo in tampered copies of Telegram X, an Android app from Telegram. At the time, the company estimated that more than 58,000 devices were infected.
The Hacker News compared the two reports. Doctor Web’s technical description of Baohuo lists the same code namespace, com.ucreator.tgjar, the same command-and-control (C2) server, and matching command names as Ovi’s analysis.
Ovi’s analysis, published October 21, 2026, does not mention Doctor Web’s findings, and Doctor Web did not name the kit. It is not clear whether the kit’s makers or one of their customers ran the campaign Doctor Web tracked.
Who Is Exposed
The tampered apps spread through sideloading, where a person installs an app file directly instead of from an app store, and through social engineering, Ovi found. He could not confirm how every victim was infected.
A second route is the kit makers’ own container app, called 洋葱盒子 (“Onion Box”), which runs other apps inside itself.
Some of the tampered Telegram X copies use the same package name as the real app on Google Play, so the name alone does not give them away.

Doctor Web found that Baohuo copies had been spreading since mid-2024 through in-app ads that led to fake app store sites. Those sites promoted Telegram X as a dating and video chat app.
The sites’ banners were available only in Portuguese, for users in Brazil, and in Indonesian. Even so, Doctor Web’s 2025 map of infected devices by country put India first, at 22.8%, ahead of Brazil at 20.5% and Indonesia at 9.6%.
Baohuo copies also turned up in the third-party stores APKPure, ApkSum and AndroidP. On APKPure, one was listed under the official developer’s name, although its digital signature was different.
Ovi got access to one of the kit’s command servers. It held data on victims apparently located in China and the United States, but not enough for a reliable count. He calls his report “an analysis of technical capability, not a measurement of victim impact.”
The apparent targets, still unconfirmed, are users of mobile wallets and messaging apps in China and Southeast Asia, including WeCom, QQ, WhatsApp, LINE, Zalo, KakaoTalk, Viber, GCash and MoMo. He found code supporting about 20 apps, but has published code only for Telegram and WeChat.

The kit’s hooking engine is the part that lets its code intercept an app’s functions. Ovi checked it on a Pixel 10 Pro running Android 17. It could not find an internal Android function it relies on, because newer Android versions changed that function.
Another tool, Frida, could still hook apps the same way on that phone. Ovi therefore describes this as extra work for the kit’s makers, not proof that Android 17 blocks the attack.
The newest sample, dated July 29, 2026, still carried the old engine. He recovered samples built for Android 16 but did not report testing that version. He has not tested phones from Chinese makers.
How It Takes Over a Telegram Account
Inside a tampered Telegram app, the kit’s code starts with the app and runs with the app’s own identity and permissions, Ovi found. That gives it the same access as the signed-in app.
Each tampered app also runs a local command server inside itself. The code for each target app is downloaded after installation, which makes the installer file harder to analyze on its own.
Attackers can send any database query to the app’s message store and get chat history back.
Telegram’s two-step verification (2FA) password is entered in the app, which uses it to generate a login proof on the phone. The kit hooks that step and copies the password in readable form before the app hashes it.
With the password, the code can reset the account’s logged-in sessions, change the linked phone number, or delete the account. Other parts of the code are designed to lock out the owner while keeping the attacker’s session alive.
The code can also hide the attacker’s session from the device list that the tampered app shows the user.
Doctor Web’s description of Baohuo covers the same device-hiding. The backdoor also sends the account’s phone number, name and password to its server every three minutes.
Neither Ovi nor Doctor Web says whether a hidden session still appears on the user’s other, untampered Telegram apps. Neither gives steps for securing an account taken over this way.
Ovi says the code shows what the kit can do, not that attackers have used every step from start to finish.
Earlier Android malware has also run legitimate apps with attacker code inside them. FjordPhantom did this to banking apps through virtualization in 2023, and so did the GodFather banking trojan in 2025.
Ovi argues the kit is different because it is sold as a product. Customers can steer it remotely against any app its makers write a module for.
The WeChat Part and the Leaked Back End
For WeChat, the kit can also use app virtualization, running the unchanged app inside its own container, Ovi found. A command copies out the account’s login identity. The app’s data is then zipped and uploaded, and a bundled login script is used to clone the account.
This part goes after the account itself, not its chat history.
Ovi and another researcher, Jurre, also found the back-end code behind the kit on a self-hosted GitLab server. It was the one part of the setup not limited to approved IP addresses.
The code shows a cloud console that merchants and resellers rent. Every command carries the customer’s ID, so each customer aims its own share of the phone fleet at victims it picks.
Commands go to phones in the kit’s phone farm, a set of phones the operation controls, and to victims’ phones. There, the kit captures login authorizations, adds friends in bulk, collects contact and profile data, and backs up whole accounts.
A scheduler sets time windows, random daily limits, and per-account budgets, so the activity looks human and gets past the platforms’ risk checks. The code calls this “account cultivation,” in Ovi’s translation.
About three dozen developers, all working on China time, appear in the code’s history, and some were still adding changes in October 2026.
The leaked back end covers personal WeChat and WeCom accounts. Ovi says it did not appear to cover Telegram, and only one of several GitLab servers was exposed.
Who Is Behind It
Ovi ties parts of the operation to three companies in Hunan province, China. One is linked to the kit’s brand website and a server certificate, another to a government website filing for a command server, and the third to the signature on the kit’s Windows control program.
He says a shared owner is “plausible, but remains unproven.”

The makers’ own name for the product is YingGai, and the product line appears in records dating back to September 2021. The samples Ovi studied date from 2024 to July 2026.
Ovi assumes the kit is used for financially motivated crime, given its focus on wallets and one-time passcodes. Doctor Web described Baohuo as “a tool for boosting the number of subscribers in Telegram channels.”
Indicators of Compromise
The kit leaves two traces on a phone that Ovi calls reliable. One is a code file, TgJarPine.dex, in the assets of some tampered Telegram copies. The other is the original app copy that LSPatch, an off-the-shelf patching tool, leaves at cache/lspatch/origin/*.apk.
Because that second trace comes from LSPatch itself, it can also appear in apps patched with the tool for other reasons.
When The Hacker News checked DNS records on October 23, 2026, several of the kit’s server and download domains no longer resolved. The domain for its version-upload server still pointed to 121.37.194[.]194.
The kit’s indicators include:
- SHA-256:
2fc4bad71eda25b9022ea7cb090d6419911ecd67e50e746b418f8a617a980301(com.ucreator.tg, framework and command handlers) - SHA-256:
0142749a159be3e41d28f910eebf28b577a282880bd0c2383bd7404189f4ff94(com.uckj.tgx, loader) - SHA-256:
dcec9640271a782553599197bcb85367971a5bb4aa84c3787d1e49a3f4f9420e(org.thunderdog.challegram, tampered Telegram X, November 2024) - SHA-256:
805834e6b8c12e180117a1816b48e387c33b53520f5a91cbf858441dc895e717(org.telegram.messenger.web, tampered Telegram, July 2024) - SHA-256:
a90e3ab2b5cf306439a378faf7107a89196116ad7ee4ad5791c2ba8839ba21c4(org.thunderdog.challegram, tampered Telegram X) - SHA-256:
f82ac2c525d1ed82e57b3f27ae689aeda46875a893ca4c42876b3166ba66bb20(com.ucreator.va_vx, WeChat host) - SHA-256:
99c5be579d218acfd2c7e2662528e7ad32a1a605d8efd1da732c13931bc30c4c(com.ucreator.va_yjb_client, Onion Box) - SHA-256:
9c8b147f76312e651faabb1411a3270efca984dd8f33bd8ded3ea611c7c583a1(uip.exe, Windows control program) - Domain:
hpncallback.gold5play[.]com(command server, not resolving on October 23) - Domain:
hpncallback.qianxunlbs[.]com(command server, not resolving on October 23) - Domain:
telegram-apk.uzyzx[.]com(download host, not resolving on October 23) - Domain:
hw.android.videoflow[.]cn(version uploads, pointing to 121.37.194[.]194 on October 23) - IP:
159.138.237[.]10:32115(Redis server) - IP:
159.138.229[.]12:26379(Redis server) - Domain:
r-bp1jehsclgbuu48m7tpd.redis.rds.aliyuncs[.]com:65531(Redis server, WeChat part) - IP:
43.225.141[.]209(relay used by the Telegram part) - URL:
kfpt.oss-cn-hangzhou.aliyuncs[.]com/android/app/YingGai/(hook downloads)
Doctor Web has published its own indicators for Baohuo.
