

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Deutsch-Französische Einigung zu „Made in Europe“ und Autoabgasen verzögert sich – SPD erhebt Einwände – POLITICO

    October 16, 2026

    The Interview – Peter Obi, Nigerian presidential candidate: The last election was rigged

    October 16, 2026

    Reform faces questions over candidate vetting after undercover filming

    October 16, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Deutsch-Französische Einigung zu „Made in Europe“ und Autoabgasen verzögert sich – SPD erhebt Einwände – POLITICO
    • The Interview – Peter Obi, Nigerian presidential candidate: The last election was rigged
    • Reform faces questions over candidate vetting after undercover filming
    • Skechers Coupon Codes 20% Off
    • China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers
    • A planet 320 light-years away confirms what scientists long suspected
    • Trump’s Russia Diesel Deal Won’t Lower Prices
    • They fled Russia, but the West sent them back
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Friday, October 16
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    BeyondTrust patches zero-day exploited in attacks since August

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 16, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    BeyondTrust warned customers on Thursday to patch a critical flaw in its Remote Support (RS) that has been exploited in zero-day attacks since late August.

    Remote Support is the company’s enterprise-grade support solution that helps IT service desks, help desks, and customer support teams troubleshoot issues remotely.

    Tracked as CVE-2026-102764, this actively exploited authentication bypass vulnerability lets unprivileged remote attackers perform file operations on unpatched appliances and affects RS 26.2.3 or earlier. BeyondTrust patched the security issue for all Remote Support and Privileged Remote Access SaaS customers on October 8, but self-hosted installations must be patched manually if automatic updates are not enabled.

    While the company shared limited details about the vulnerability, it said the zero-day was abused in the wild by a suspected China-nexus espionage actor tracked by Mandiant and Google Threat Intelligence Group (GTIG) security researchers as “Armory Castle” (formerly UNC5221) and by cybersecurity firm CrowdStrike as “Warp Panda.”

    According to Mandiant researchers, who spotted the initial attacks, Armory Castle hackers exploited the flaw to gain initial access and escalated to root privileges on compromised devices by enabling Set User ID (SUID) permissions.

    Next, they deployed new Sawfly web shell and Bareclaw tunneler malware, wiped logs to evade detection, and moved laterally through the victim’s network using compromised Administrator credentials by opening remote sessions on downstream systems.

    “After establishing a foothold through the web shell, the actor elevated from the web service account to root-level control of the appliance host. This gave them access to every credential the appliance stored or brokered and the ability to modify files that survive reboot and configuration reset,” Mandiant said.

    “Any appliance that was reachable from the internet on a vulnerable version during the exploitation window should be treated as potentially compromised until it has been reviewed.”

    ​Internet threat watchdog Shadowserver tracks over 1,400 BeyondTrust remote support instances exposed online, but it provides no information on how many have already been secured or are honeypots.
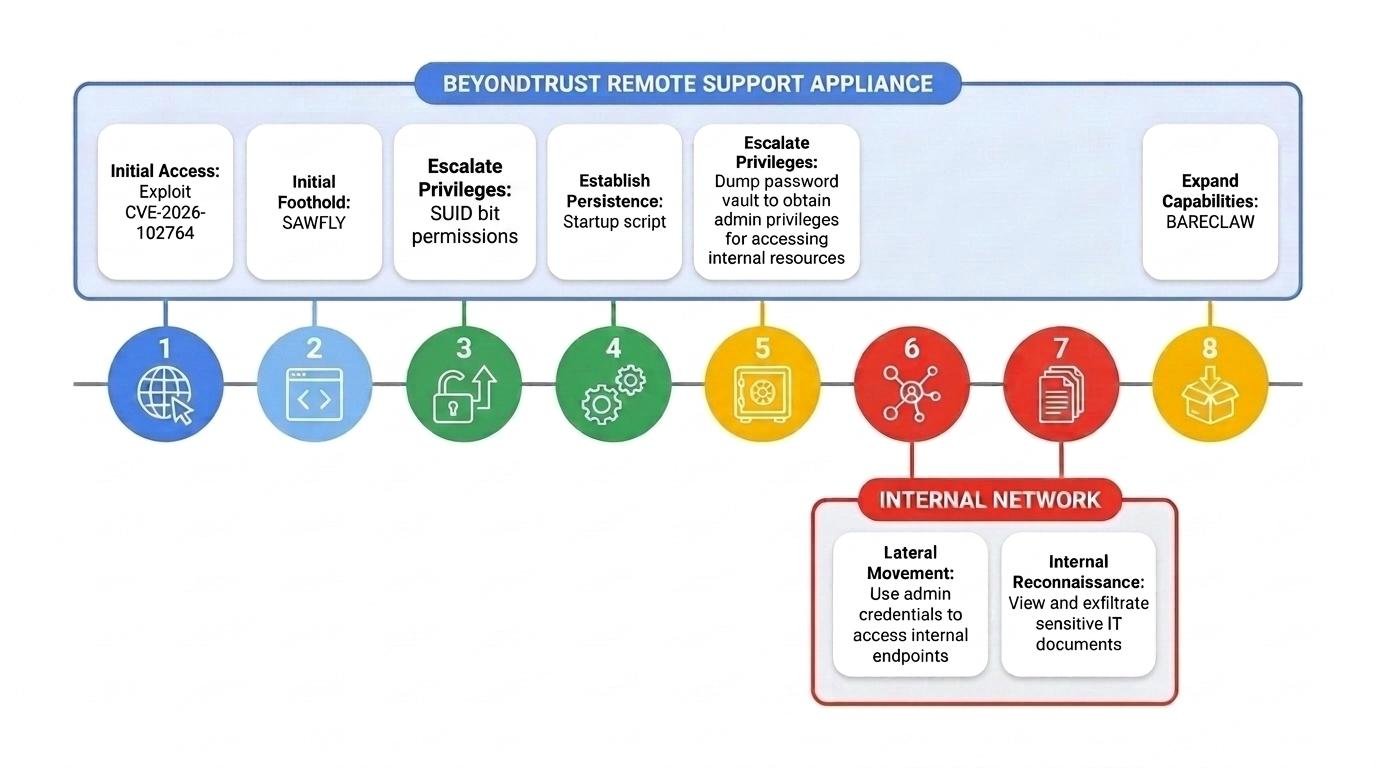
    Attack chain
    Attack chain (Mandiant / GTIG)

    Armory Castle is known for targeting zero-day vulnerabilities in network edge appliances, including various Citrix NetScaler (CVE-2023-4966) and Ivanti Connect Secure (CVE-2023-46805 and CVE-2024-21887, then CVE-2025-0282) appliances, since at least October 2023 to breach enterprise networks and drop new custom malware.

    ​Threat intelligence company Volexity also said in January 2024 that UNC5221 had backdoored more than 2,100 Ivanti appliances using the GiftedVisitor webshell in attacks chaining the CVE-2023-46805 and CVE-2024-21887 zero-days.

    “In past campaigns, ARMORY CASTLE has conducted widespread and opportunistic exploitation following the public disclosure of vulnerabilities it had exploited selectively as zero-days, racing to infiltrate target organizations before patches are deployed,” Mandiant added. “It is possible that we will observe similar widespread exploitation attempts associated with CVE-2026-102764.”

    CVE-2026-102764 is the latest in a string of other BeyondTrust flaws that threat actors have exploited in the wild in recent years. Most recently, attackers exploited another critical remote code execution vulnerability (CVE-2026-1731) affecting Remote Support and Privileged Remote Access appliances to establish WebSocket channels and deploy ransomware.

    The Chinese state-backed Silk Typhoon hacking group is also believed to have exploited two zero-days (CVE-2024-12356 and CVE-2024-12686) to breach BeyondTrust’s systems and use a stolen API key to compromise 17 Remote Support SaaS instances, including the U.S. Treasury Department’s instance.

    In the same campaign, Silk Typhoon has also targeted the Office of Foreign Assets Control (OFAC), which administers U.S. sanctions programs, and the Committee on Foreign Investment in the United States (CFIUS), which reviews foreign investments for national security risks.

    BeyondTrust provides identity security services to over 20,000 customers worldwide, including government agencies and 75% of Fortune 100 companies.

    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    attacks August BeyondTrust Exploited Patches ZeroDay
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers

    Novel Android RAT ‘Hirudo’ Replaces Banking Apps With Trojanized Copies

    Ukraine’s Budget Gap: Can Kyiv Afford Its Own Defense Amid EU Pressure and Russian Attacks?

    No click required: How the ad industry became a pipeline for mercenary spyware

    Citizen Lab Traces Zero-Click Candiru Spyware Infections at Al Jazeera to Targeted Online Ads

    Android gets AI defenses against messaging scams, fake calls

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Deutsch-Französische Einigung zu „Made in Europe“ und Autoabgasen verzögert sich – SPD erhebt Einwände – POLITICO

    October 16, 2026

    The Interview – Peter Obi, Nigerian presidential candidate: The last election was rigged

    October 16, 2026

    Reform faces questions over candidate vetting after undercover filming

    October 16, 2026

    Skechers Coupon Codes 20% Off

    October 16, 2026
    Latest Posts

    Early release scheme risks more serious crimes, probation chief warns

    August 12, 2026

    UK heatwave live: Met Office issues extreme heat warning as government convenes emergency Cobra meeting | Extreme heat

    August 12, 2026

    Rybakina defeats Osaka, advances to Canadian Open semifinals to play Gauff | Tennis News

    August 12, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Deutsch-Französische Einigung zu „Made in Europe“ und Autoabgasen verzögert sich – SPD erhebt Einwände – POLITICO

    October 16, 2026

    The Interview – Peter Obi, Nigerian presidential candidate: The last election was rigged

    October 16, 2026

    Reform faces questions over candidate vetting after undercover filming

    October 16, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.