

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Two paintings stolen from Renoir Museum in France are recovered

    October 9, 2026

    Tory tax break for banks has cost UK public purse £6bn, says TUC | Banking

    October 9, 2026

    Lib Dem MP quits frontbench job over Ed Davey’s leadership

    October 9, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Two paintings stolen from Renoir Museum in France are recovered
    • Tory tax break for banks has cost UK public purse £6bn, says TUC | Banking
    • Lib Dem MP quits frontbench job over Ed Davey’s leadership
    • Trump’s attempt to rename AI is looking awfully artificial
    • Google Cloud Launches Gemini Agent, One Universal Agent for Enterprise Work
    • Google Domains Impacted by Recent ccTLD Hijacks
    • Dragonfly Partner Rejects ‘Bunker Mode’ Doomerism, calls for proactive blockchain measures
    • Here’s a look at the Nobel Prizes for science
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Friday, October 9
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Max severity SonicWall SMA1000 flaw now exploited in attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 9, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Attackers are exploiting a maximum-severity vulnerability in SonicWall SMA1000 appliances (CVE-2026-102255) that was patched on Tuesday, three days ago.

    Tracked as CVE-2026-102255, the flaw affects the Appliance WorkPlace interface on SMA1000 6210, 7210, and 8200v models, but does not affect the SMA 100 Series product line or SSL-VPN running on SonicWall firewalls.

    “By abusing this path, a remote unauthenticated attacker could potentially exploit this vulnerability to direct the appliance to issue requests on their behalf and reach internal functionality and perform unauthorized operations,” SonicWall explained.

    While SonicWall has not yet flagged this vulnerability as actively exploited in its Tuesday advisory, Previdian founder and security researcher Ryan Dewhurst told BleepingComputer on Friday that the company’s honeypot network has detected exploitation attempts consistent with the CVE-2026-102255 flaw.

    “The requests targeted the WorkPlace Extraweb interface, using a crafted OPTIONS request to reach the appliance’s internal CouchDB service at 127.0.0.1:5984. The payload attempted to traverse into a CouchDB design document and invoke its _rewrite function, while supplying an HTTP Basic Authorization header containing the credentials admin:admin,” Dewhurst told BleepingComputer.

    “It affects the same WorkPlace interface targeted by earlier SSRF vulnerabilities disclosed in July and September 2026. However, the October vulnerability uses a different exploitation technique.

    Dewhurst also added that while this activity is consistent with active exploitation attempts, Previdian has not yet established “whether those attempts would have successfully compromised any systems.”

    While Internet threat watchdog Shadowserver now tracks more than 400 SMA1000 appliances exposed online, there is no information on how many are honeypots or have already been patched against CVE-2026-102255 attacks.
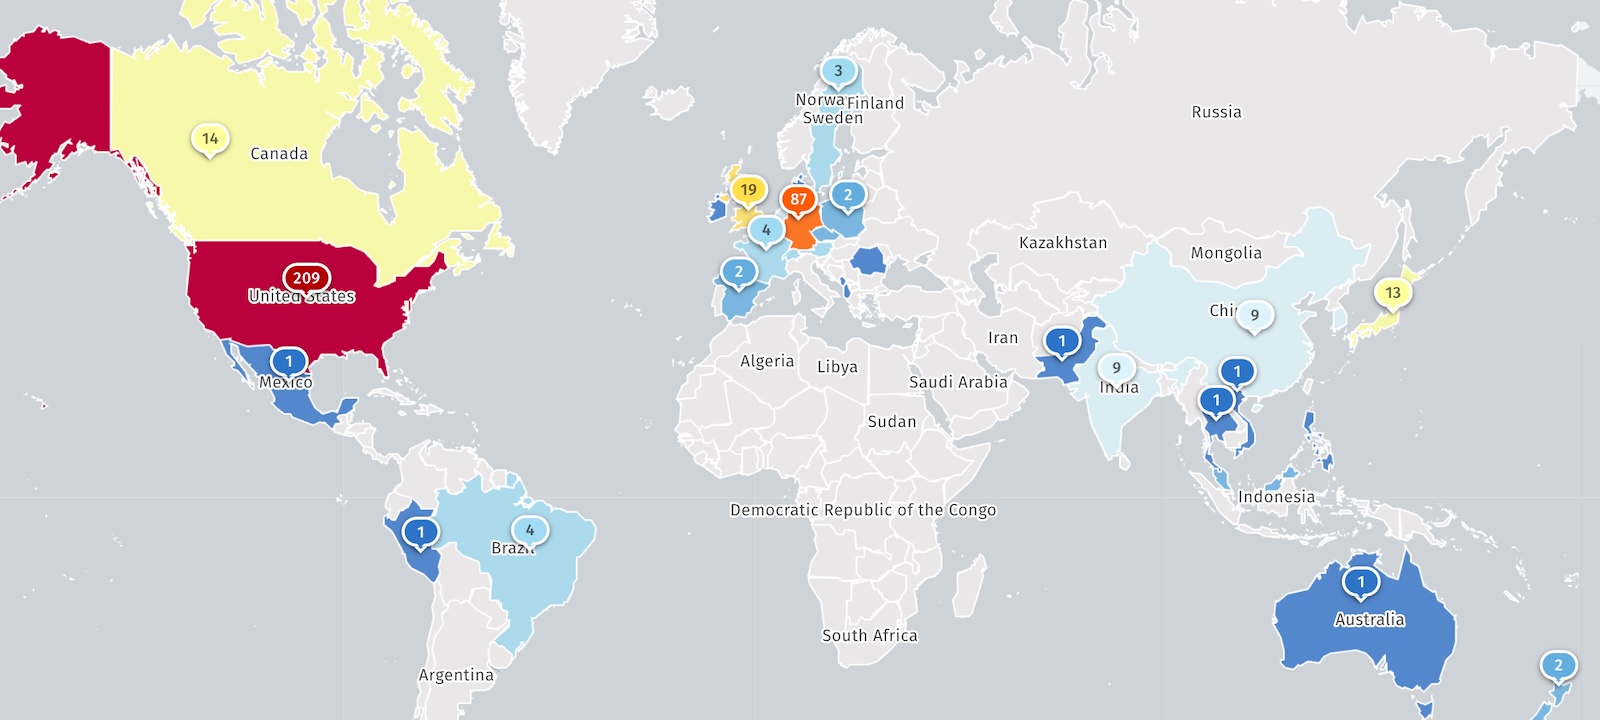
    SMA1000 instances exposed online
    SMA1000 instances exposed online (Shadowserver)

    ​SMA1000 enterprise-grade secure remote access gateways are often targeted because Managed Service Providers (MSSPs), many large corporations, and government agencies use them for VPN access to internal apps and corporate networks.

    For instance, in July, threat actors abused two SMA1000 zero-days (CVE-2026-15409 and CVE-2026-15410) for weeks to install custom Sou5, OrangeTail, and RootRun malware on vulnerable VPN appliances.

    The U.S. Cybersecurity and Infrastructure Security Agency (CISA) later linked some of these attacks to ransomware gangs.

    Last month, SonicWall also warned customers that attackers were chaining two new zero-days (CVE-2026-83548 and CVE-2026-83549) in the wild to execute remote code on vulnerable SMA1000 gateways.

    Over the last four years, CISA has added 19 SonicWall vulnerabilities to its catalog of actively exploited flaws, flagging 13 of them as used by ransomware gangs.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    attacks Exploited Flaw Max severity SMA1000 SonicWall
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Google Domains Impacted by Recent ccTLD Hijacks

    In Other News: AI Used in Korean Bank Breaches, Poem-Guided Botnet, Empire Admin Gets 40 Years

    Man admits to running network of 15,000 money mules for cybercriminals

    Microsoft: Outdated Windows devices will stop receiving security updates

    FBI Seizes 7 Domains, Disrupts Flax Typhoon Tools Used in Critical Infrastructure Intrusions

    Anthropic Fast-Tracks AI Bug Reports to OSS Maintainers, Taps 11 Firms for OT Security

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Two paintings stolen from Renoir Museum in France are recovered

    October 9, 2026

    Tory tax break for banks has cost UK public purse £6bn, says TUC | Banking

    October 9, 2026

    Lib Dem MP quits frontbench job over Ed Davey’s leadership

    October 9, 2026

    Trump’s attempt to rename AI is looking awfully artificial

    October 9, 2026
    Latest Posts

    Reform donor Arron Banks urged to set out extent of surveillance of journalists | Arron Banks

    August 10, 2026

    The Canadian Secessionists Who Love Trump

    August 10, 2026

    How ‘Harry Potter’ Fans Protected Dobby’s Grave From the Path of a U.K.-Ireland Power Line

    August 10, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Two paintings stolen from Renoir Museum in France are recovered

    October 9, 2026

    Tory tax break for banks has cost UK public purse £6bn, says TUC | Banking

    October 9, 2026

    Lib Dem MP quits frontbench job over Ed Davey’s leadership

    October 9, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.