

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    If a data center is camouflaged in the woods, will anyone hate it?

    October 2, 2026

    OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling

    October 2, 2026

    Bitcoin treasuries may struggle to match Strategy

    October 2, 2026
    Facebook X (Twitter) Instagram
    Trending
    • If a data center is camouflaged in the woods, will anyone hate it?
    • OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling
    • Bitcoin treasuries may struggle to match Strategy
    • NASA’s Curiosity rover just hit 5,000 days on Mars and sent back this stunning view
    • Chesapeake Bay Restoration Obstructed by Federal Policy Shift, Tribal Withdrawal
    • Here’s How Easy It Was for Journalists to Start Two Private Schools — ProPublica
    • Should we refuse to give the Bayeux tapestry back to France? Of course not! So why are we keeping the Parthenon marbles? | Simon Jenkins
    • Washington’s diplomacy in Sudan has backfired | Opinions
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Friday, October 2
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Attackers Abuse MSP360 to Deploy ScreenConnect in Dual-RMM Phishing Attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 1, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananSep 30, 2026Endpoint Security / Social Engineering

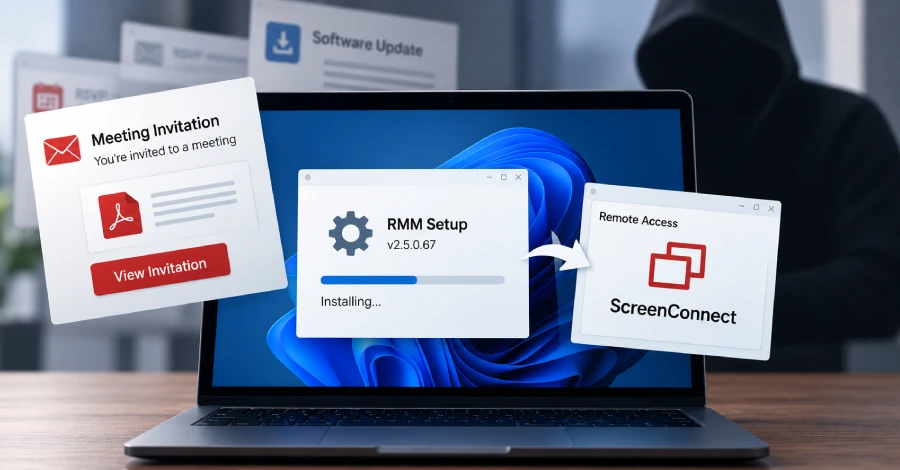
    Microsoft has warned of phishing campaigns distributing an installer for the MSP360 Remote Monitoring and Management (RMM) software under the guise of meeting invitations, PDF-themed lures, software update prompts, and other social-engineering content.

    “Once executed, the legitimate MSP360 installer, distributed under a deceptive file name established remote management access on affected devices and enabled threat actors to gain an initial foothold using trusted administrative software,” the Microsoft Security Research team said.

    The initial foothold is then used to download and install a ConnectWise ScreenConnect client, offering threat actors a redundant remote-access channel to compromised endpoints. The access is then abused to deliver additional tools and carry out information collection and credential-access operations. The activity has not been attributed to any known threat actor or group.

    Cybersecurity

    The multi-stage intrusion chain, which the Windows maker detected in July 2026, begins with phishing emails distributing a digitally signed MSP360 RMM v2.5.0.67 installer under deceptive names such as below –

    • VIP_ECARD_INVITATION_rmm_v2.5.0.67_oid[redacted].exe
    • ZoomSetup_Installation_v2.5.0.67_ oid[redacted].exe
    • PDF Reader & Editor the Adobe Acrobatte_rmm_v2.5.0.67_ oid[redacted].exe
    • RSVP_INVITATION_E_CARD_rmm_v2.5.0.67_ oid[redacted].exe
    • SSA.GOV_STATEMENT_rmm_v2.5.0.67_ oid[redacted].exe

    The installer packages are staged on attacker-controlled infrastructure and legitimate cloud services including Amazon S3, Cloudflare R2, Dropbox, GitLab, and Supabase.

    Once launched, the installer drops multiple DLLs, while relaunching itself by invoking the Windows User Account Control (UAC) elevation workflow to run in a privileged context, establish persistent access by deploying MSP360, and leverage the RMM tool to execute PowerShell for stealthily installing ScreenConnect.

    The installer also enumerates installed .NET runtimes and registers two Windows services (RMM.Agent.exe and RMM.Agent.Launcher.exe) and creates Registry-based autorun entries to ensure that MSP360 is automatically launched when users sign-in to the machine.

    Furthermore, it modifies the Windows Firewall configuration to allow inbound UDP traffic to MSP360 (i.e., RMM.Agent.exe) on port 48678.

    The dual-RMM remote access attack enables the attacker to transfer additional executables and facilitate post-compromise activity, while camouflaging malicious activity within regular remote administration workflows. The payloads are run through ScreenConnect’s native RunFile functionality.

    Cybersecurity

    Microsoft said it also observed a separate set of attacks in July 2026 that switched MSP360 for Faronics Deploy Agent to find a way in, and then used it to download and install ScreenConnect. This suggests that the threat actors are putting multiple RMM tools for remote access.

    “This activity highlights how threat actors continue to abuse legitimate remote administration software to blend into normal IT operations while maintaining persistent access and reducing detection opportunities,” Microsoft said.

    “The combination of MSP360 and ScreenConnect provided the threat actor with redundant remote administration channels and enabled the transfer, execution, and management of additional tooling during subsequent stages of the intrusion.”

    Abuse Attackers attacks Deploy DualRMM MSP360 Phishing ScreenConnect
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling

    Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools

    Microsoft’s X account hacked in crypto pump-and-dump scheme

    Rolling the cyber dice with open-source and open-weight AI models

    Exploited Fortinet FortiMail Zero-Day Calls for Urgent Action

    Microsoft says threat actors are ahead in the early AI race

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    If a data center is camouflaged in the woods, will anyone hate it?

    October 2, 2026

    OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling

    October 2, 2026

    Bitcoin treasuries may struggle to match Strategy

    October 2, 2026

    NASA’s Curiosity rover just hit 5,000 days on Mars and sent back this stunning view

    October 2, 2026
    Latest Posts

    Max Miller Continues to Resist Pressure to Drop Out as Deadline Looms

    August 7, 2026

    Houthi attacks kill at least 10 in Yemen as rebels target oil-rich Marib

    August 8, 2026

    Scientists find unexpected life on Ötzi the Iceman’s 5,300-year-old body

    August 8, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    If a data center is camouflaged in the woods, will anyone hate it?

    October 2, 2026

    OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling

    October 2, 2026

    Bitcoin treasuries may struggle to match Strategy

    October 2, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.