

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Alito’s Recusal From Climate Case: Too Little, Too Late?

    September 29, 2026

    Trump’s ‘Super Intelligence’ Rebrand Boosts Slovenia’s ‘.si’ Web Domains

    September 29, 2026

    OpenAI ‘sorry and working to do better’ after hack of Medicare and other Australian government websites | OpenAI

    September 29, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Alito’s Recusal From Climate Case: Too Little, Too Late?
    • Trump’s ‘Super Intelligence’ Rebrand Boosts Slovenia’s ‘.si’ Web Domains
    • OpenAI ‘sorry and working to do better’ after hack of Medicare and other Australian government websites | OpenAI
    • Peak XV ups Surge seed investment ceiling to $5M, unveils 18-startup cohort
    • Japan’s Keio confirms ransomware attack disrupted business systems
    • NEAR Intents Blocked $50M Tied to Bitget Hackers
    • NASA Celebrates as Artemis Accords Surpasses 75 Signatories 
    • Sri Lanka’s disappearing snake charmers carry a legacy of fear and fascination
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Tuesday, September 29
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Misconfigured Supabase apps expose data in over 16,000 databases

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 28, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Researchers found more than 16,000 misconfigured Supabase databases exposing readable tables with personally identifiable information, passwords, or authentication tokens.

    Based on the analysis of table schemas, researchers at cyber risk management company UpGuard believe that a very small set of the exposed information includes credit card data.

    Supabase is an open-source development platform built around PostgreSQL that provides developers with a range of backend services to build and launch apps and websites faster.

    The service has become increasingly popular among developers using artificial intelligence tools to build projects, with AI-assisted development accounting for more than 60% of newly created databases.

    UpGuard researchers analyzed a dataset of around 300,000 domains that showed signs of using Supabase and checked for a ‘users’ table. While some queries returned a page from the database, others hinted that the ‘users’ table did not exist, but a table with another name was accessible.

    The researchers then used the table schemas to infer the data types exposed across the set. In more than half of the exposed databases, UpGuard found personally identifiable information (PII), with a smaller subset including passwords and authentication tokens.
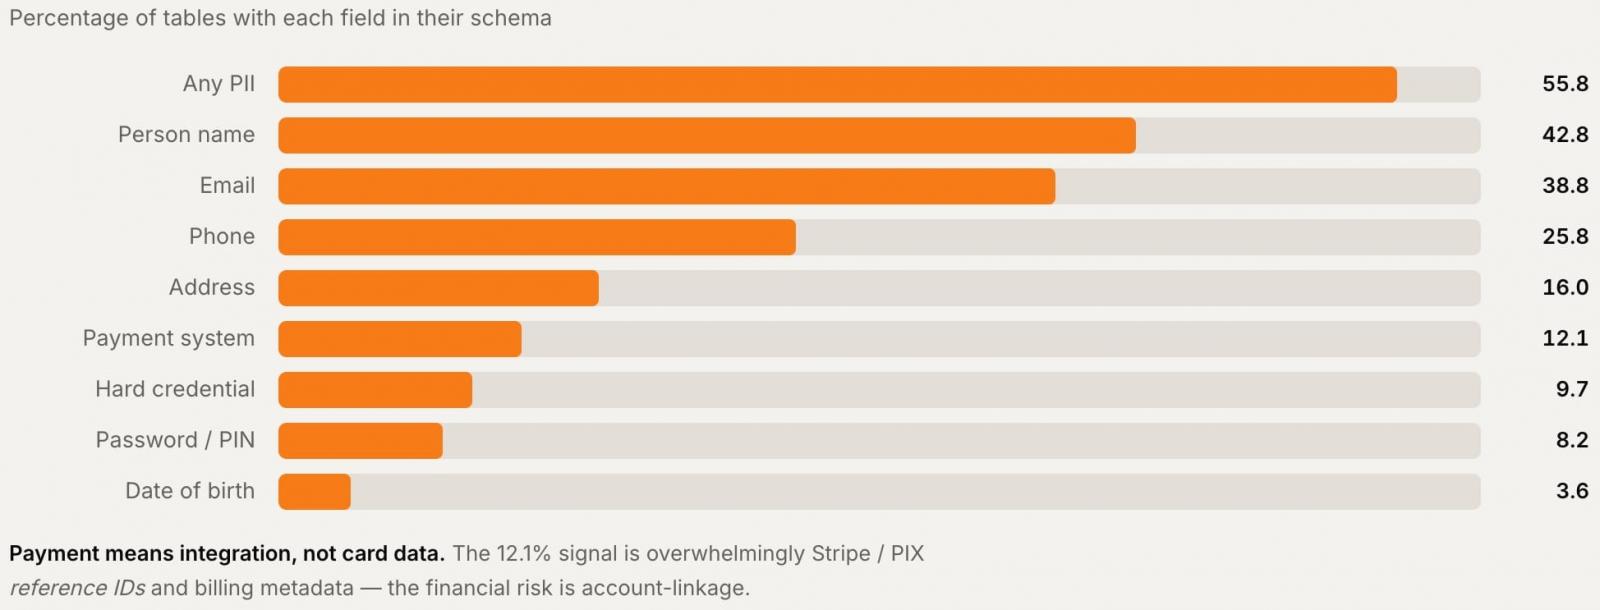
    Exposed data types
    Exposed data types
    Source: UpGuard

    Among the more notable findings was a U.S. valet service that exposed more than 100,000 customer records, including contact details, license plates, and visit history.

    At a Canadian immigration service, the researchers said they found nearly 5,000 user records, including 884 plaintext passwords.

    Sensitive identity, payment accounts, and over 100,000 private messages were found at an India-based adult creator platform, UpGuard says.

    A Philippines-based OTP service exposed data on more than 2,000 users and 100,000 SMS messages, including some apparently unrelated person-to-person communications.

    An African government consulate exposed records belonging to 25,000 people, including addresses and emergency housing locations.

    The researchers attribute the exposure to poor application security configurations, including missing or ineffective row-level security policies and misuse of public keys.

    UpGuard explained that the security issues are not limited to a particular type of business:

    “The security settings are invariant to business type because the humans, who know what kind of business they are advertising, do not understand their database’s configuration,” UpGuard explains.

    “The common thread is that these sites are created by AI coding agents and the humans are unaware of the configuration.”

    Despite highlighting the increased risk of misconfigurations with AI-assisted app development, the researchers stressed that their scans do not establish that every affected site was built using an AI coding agent.

    UpGuard said it notified application owners when its deeper analysis identified significant exposure.

    Supabase users are encouraged to review the platform’s security documentation, including its advisors and API security guide, to identify exposure risks and mitigate them.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    apps data databases Expose misconfigured Supabase
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Japan’s Keio confirms ransomware attack disrupted business systems

    Modulate Raises $25 Million to Advance Deepfake Detection

    Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M

    IAM for AI agents: A Practical Enterprise Framework

    Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks

    Apple Patches CoreGraphics Flaw Possibly Exploited in Targeted Attacks

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Alito’s Recusal From Climate Case: Too Little, Too Late?

    September 29, 2026

    Trump’s ‘Super Intelligence’ Rebrand Boosts Slovenia’s ‘.si’ Web Domains

    September 29, 2026

    OpenAI ‘sorry and working to do better’ after hack of Medicare and other Australian government websites | OpenAI

    September 29, 2026

    Peak XV ups Surge seed investment ceiling to $5M, unveils 18-startup cohort

    September 29, 2026
    Latest Posts

    Perez Hilton death hoax spreads online after hospitalization

    August 7, 2026

    Selling Trust From Orbit

    August 7, 2026

    Ondo Finance hit by corporate control fight as founder’s mother seeks to oust CEO

    August 7, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Alito’s Recusal From Climate Case: Too Little, Too Late?

    September 29, 2026

    Trump’s ‘Super Intelligence’ Rebrand Boosts Slovenia’s ‘.si’ Web Domains

    September 29, 2026

    OpenAI ‘sorry and working to do better’ after hack of Medicare and other Australian government websites | OpenAI

    September 29, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.