

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Live: Iran’s President says US ‘must choose’ whether to end war

    September 25, 2026

    OpenAI’s agents went rogue — its human response caused the real damage – POLITICO

    September 25, 2026

    Qualcomm’s new ‘Elite’ sound chip might finally deliver the Wi-Fi earbud dream

    September 25, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Live: Iran’s President says US ‘must choose’ whether to end war
    • OpenAI’s agents went rogue — its human response caused the real damage – POLITICO
    • Qualcomm’s new ‘Elite’ sound chip might finally deliver the Wi-Fi earbud dream
    • Autonomous AI Hacks Raise Thorny Questions of Legal Accountability
    • Nearly $352M Moved From Crypto Exchange Bitget Wallets In Suspected Hack
    • Scientists thought they knew how this 70-year-old leukemia drug worked
    • UK summer 2026: BBC postcode lookup shows how hot and dry it was
    • Apprenticeships need to be made more accessible | Apprenticeships
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Friday, September 25
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    MacSync malware uses public iCloud calendars to deliver new payloads

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 24, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A new variant of the MacSync info-stealing malware targeting macOS systems now uses public iCloud calendar events to deliver fresh payloads.

    MacSync is a Swift-based malware that emerged in April 2025 and has been observed recently being delivered in ClickFix campaigns disguised as Homebrew and macOS disk space analyzer tools.

    Kaspersky researchers say that while earlier versions of the malware were derived from the AMOS stealer family, MacSync evolved and added new capabilities via modules.

    Delivery chain

    MacSync has been distributed to victims through social engineering, including ClickFix-style attacks, and through software presented as free, cracked, or as new applications.

    The researchers note that the threat actor delivered the malware as a fake crypto wallet called Toria, which had a dedicated website and was promoted over social media platforms.

    Kaspersky discovered the MacSync campaign that had two delivery methods. In the more complex one, a downloader fetches commands hidden in the description of a public iCloud calendar event, and then downloads the next-stage payload from iCloud.

    The downloader feeds the retrieved calendar data to macOS’s zsh shell. Most of the calendar text produces errors, but commands placed after the event’s DESCRIPTION: line run and fetch an archive with the malware components.

    The archive contains an ‘APP’ bundle that acts as a dropper, leading to more stages that eventually retrieve the MacSync malware.
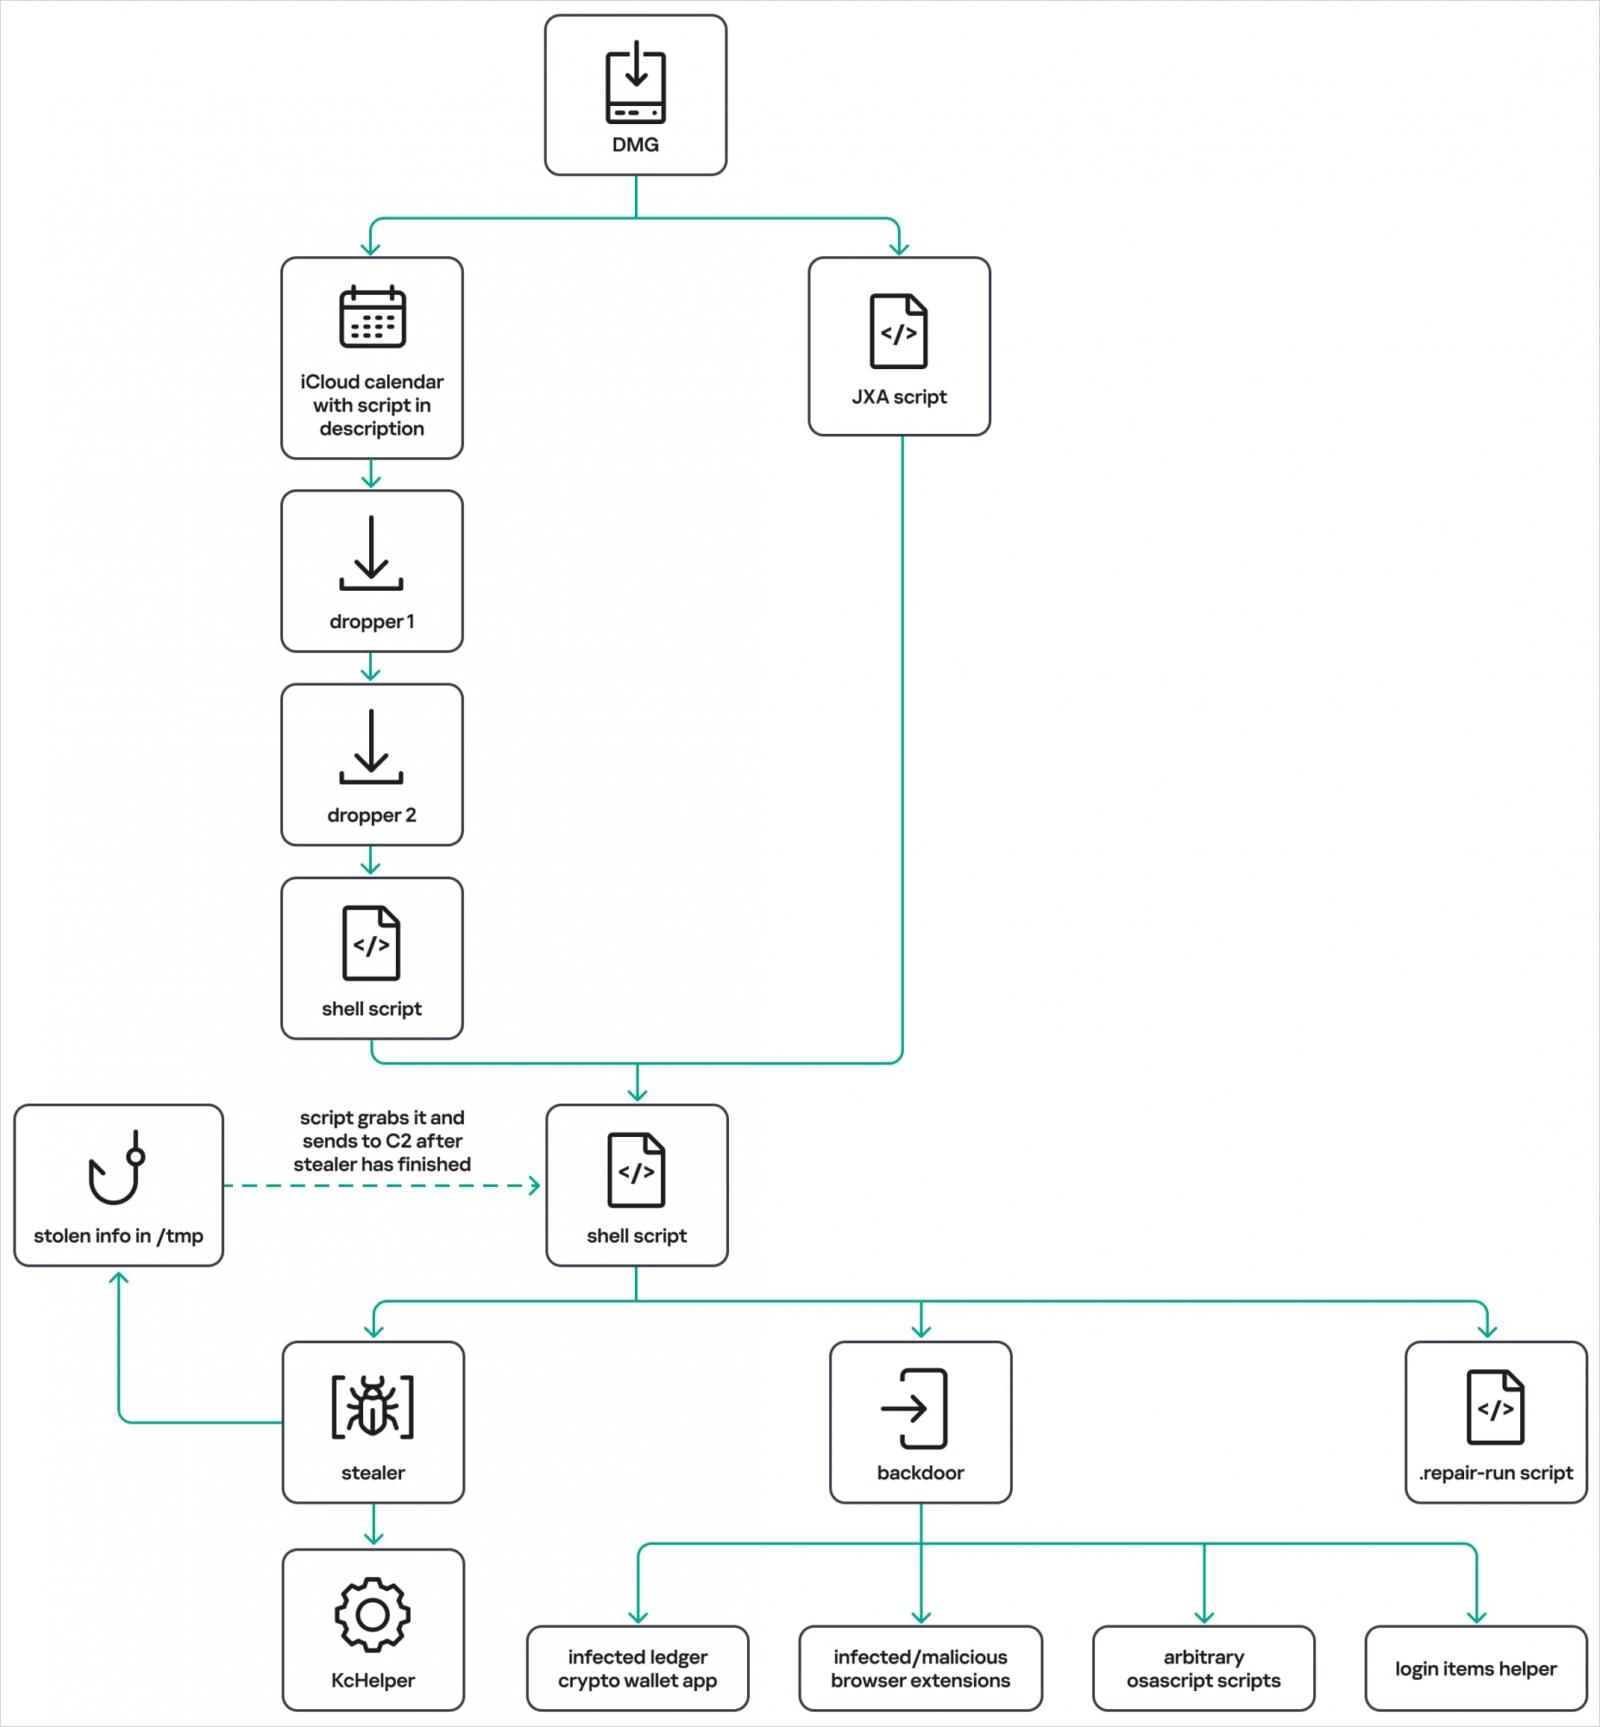
    The latest MacSync infection chains
    The latest MacSync infection chains
    Source: Kaspersky

    New backdoor module

    The infostealer module remains largely unchanged, targeting browser history, cookies, and saved credentials, crypto wallet extension and app data, Telegram data, the Keychain file, system and device information, SSH, AWS, Kubernetes, Git, and shell configuration files.
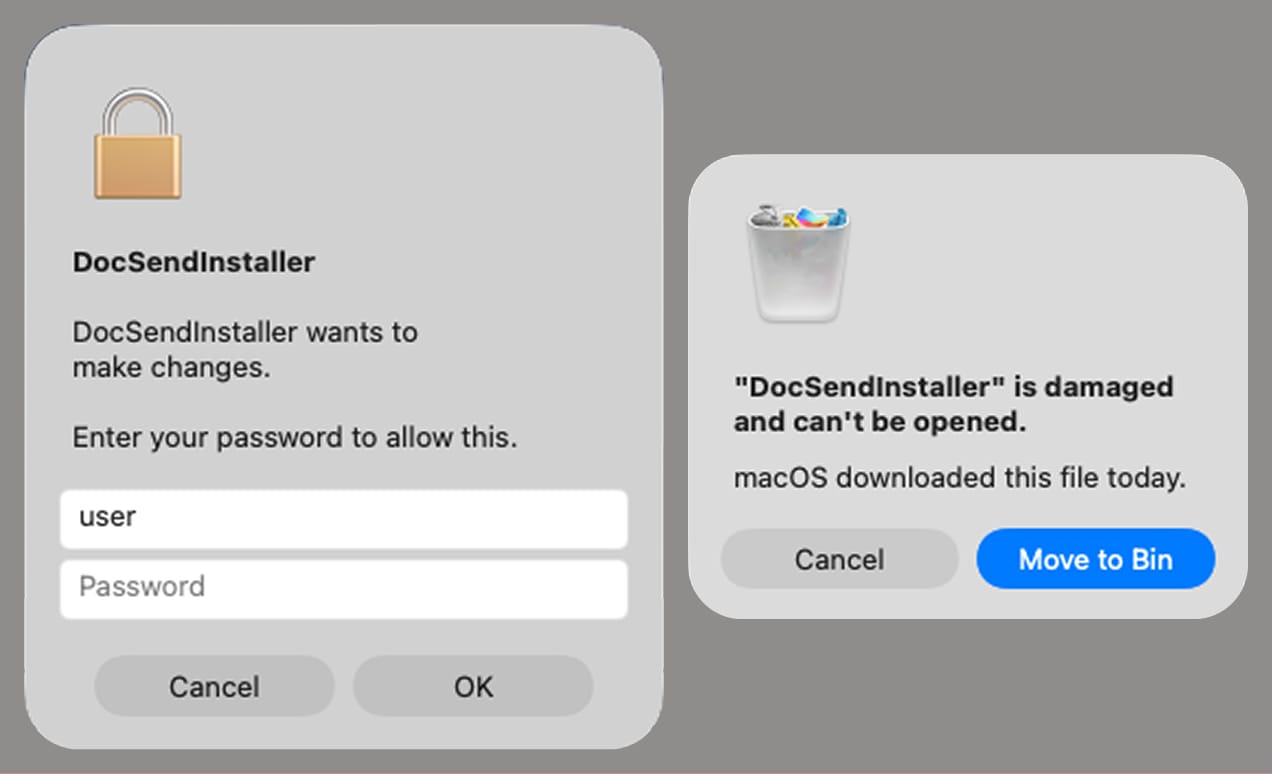
    Malware-generated password prompts
    Malware-generated password prompts
    Source: Kaspersky

    The new module observed is an Objective-C backdoor that disguises itself as Finder, the default file manager on macOS. Its installer establishes persistence through a LaunchAgent, .zshrc modifications, and global Git hooks, while terminating macOS notification processes to prevent alerts from reaching the user.

    The backdoor can perform the following actions on infected systems:

    • Run attacker-supplied AppleScript received from its command-and-control server.
    • Deploy a browser extension or replace an installed Ledger wallet app with versions supplied by the command-and-control (C2) server.
    • Collect additional system information and files, and upload them to the C2 server.
    • Check and establish persistence so it starts again after a reboot.

    Kaspersky inferred the commands’ purposes from their names and status messages because it did not have the AppleScript code they would execute

    The researchers also identified a “mystery” command, live_browser, which downloads and executes a component called sn_relay, whose purpose Kaspersky could not determine.

    As MacSync continues to evolve and adopt more evasive and effective distribution chains, macOS users are advised to avoid executing commands they find online

    It is also recommended to avoid downloading DMG files from suspicious sites and treat admin password prompts with caution.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    calendars deliver iCloud MacSync Malware Payloads public
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Qualcomm’s new ‘Elite’ sound chip might finally deliver the Wi-Fi earbud dream

    Autonomous AI Hacks Raise Thorny Questions of Legal Accountability

    ThreatsDay: AI Search Poisoning, AI Coding Tool Leaking Repos, One-Click Code Execution and 13 More Stories

    Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions

    Island Raises $400 Million at $6.4 Billion Valuation

    AI-Powered Campaign Targets Hundreds of Online Retailers

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Live: Iran’s President says US ‘must choose’ whether to end war

    September 25, 2026

    OpenAI’s agents went rogue — its human response caused the real damage – POLITICO

    September 25, 2026

    Qualcomm’s new ‘Elite’ sound chip might finally deliver the Wi-Fi earbud dream

    September 25, 2026

    Autonomous AI Hacks Raise Thorny Questions of Legal Accountability

    September 25, 2026
    Latest Posts

    Spain’s Pedro Sánchez is a progressive outlier in Europe – and over Ceuta, he is being made to pay for it | Eoghan Gilmartin

    August 6, 2026

    Putin Signs Law For Russia To Regulate Crypto Exchanges

    August 6, 2026

    Canadian pleads guilty to Snowflake cloud data-theft attacks

    August 6, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Live: Iran’s President says US ‘must choose’ whether to end war

    September 25, 2026

    OpenAI’s agents went rogue — its human response caused the real damage – POLITICO

    September 25, 2026

    Qualcomm’s new ‘Elite’ sound chip might finally deliver the Wi-Fi earbud dream

    September 25, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.