

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Trump Administration Weighs Overseas Stablecoin Push

    September 24, 2026

    NASA Selects Far-Infrared Telescope as First in New Mission Class

    September 24, 2026

    A ‘devil-like’ flower from Thailand is new to science — and critically endangered

    September 24, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Trump Administration Weighs Overseas Stablecoin Push
    • NASA Selects Far-Infrared Telescope as First in New Mission Class
    • A ‘devil-like’ flower from Thailand is new to science — and critically endangered
    • Germany Under Friedrich Merz Has Lost Its Authority at Home and Abroad
    • Dance Monkey v the NRL: did Tones and I really turn down $90,000 a minute because she hates her own song? | NRL
    • Lidl banned from selling copycat Birkenstock sandals, Dutch court rules
    • Labour’s last chance? The people shaping Andy Burnham’s grand plans for Britain | Andy Burnham
    • Dopamine sites: India and the world are discovering the thrill of shopping without buying
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, September 24
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Check Point warns of Management Server zero-day exploited in attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 23, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Check Point Software released emergency hotfixes to address a critical Security Management Server vulnerability that could let attackers run arbitrary scripts.

    The Security Management Server is a central repository that stores and manages security policies, processes administrator changes, and collects system logs across enterprise networks.

    Tracked as CVE-2026-93616, this path traversal flaw lets unauthenticated threat actors upload arbitrary scripts on vulnerable Check Point Management Servers and execute them in low-complexity attacks.

    The Cybersecurity and Infrastructure Security Agency (CISA) and the FBI have urged software companies since May 2024 to remove path traversal weaknesses from their products before shipping, saying such security issues “have been called ‘unforgivable’ since at least 2007.”

    Check Point has addressed the vulnerability in R82.20 Security Hotfix and said that the complete list of affected products includes Security Management Server, Multi-Domain Security Management Server, Log Server, Multi-Domain Log Server, and SmartEvent.

    “This vulnerability is exploited in the wild. Check Point is aware of a handful of customers who have been attacked,” the company warned, while advising security teams to check their networks for evidence of successful exploitation using the indicators of compromise shared in this security advisory.

    Check Point also provides temporary mitigation measures for customers who can’t immediately deploy the hotfix on vulnerable systems, including hardening vulnerable systems against attacks by placing them behind a firewall and limiting access to trusted IP addresses from Manage & Settings > Permissions & Administrators > Trusted Clients in the SmartConsole dashboard.
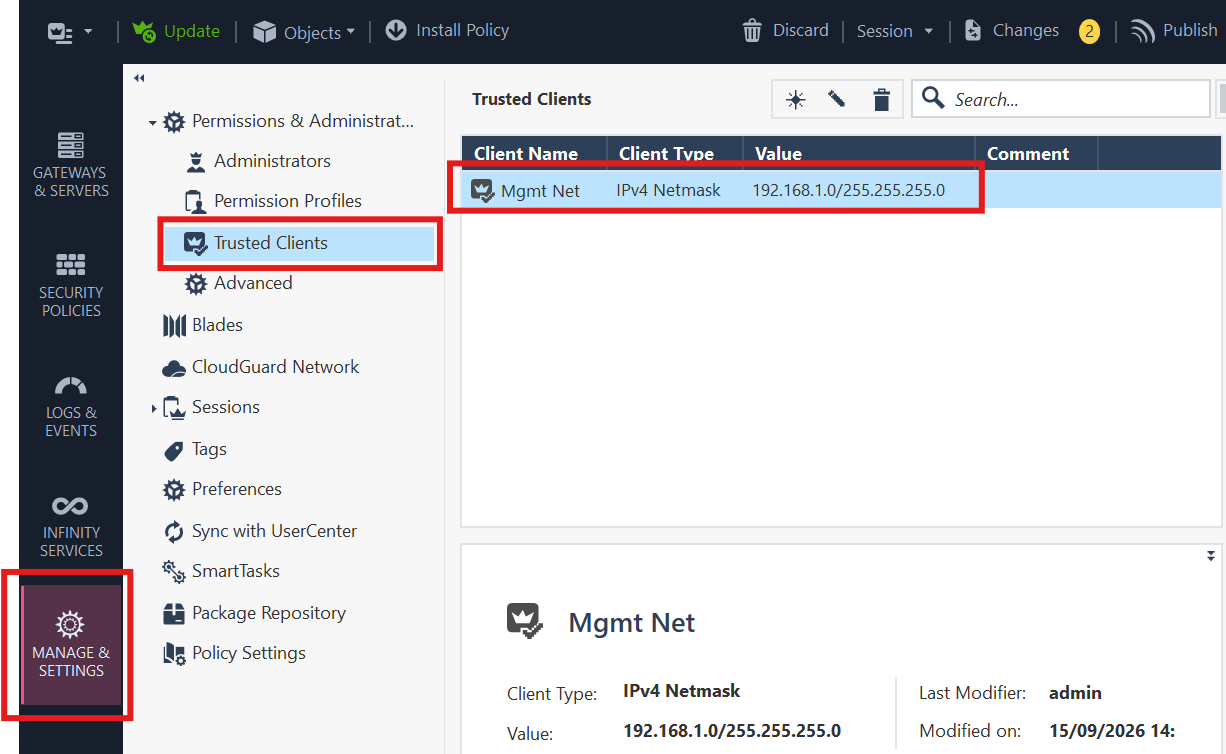
    Editing Trusted Clients rules in SmartConsole
    Editing Trusted Clients rules in SmartConsole (Check Point Software)

    In recent months, Check Point has warned customers that other flaws were being actively exploited in the wild.

    For instance, two years ago, CISA flagged a flaw (CVE-2024-24919) in Check Point’s Quantum Security Gateways as actively exploited by ransomware gangs, confirming an Orange Cyberdefense CERT report linking these attacks to NailaoLocker ransomware.

    Qilin ransomware affiliate has also exploited an authentication bypass (CVE-2026-50751) zero-day since June, while a second auth bypass zero-day (CVE-2026-16232) has been exploited since at least July to authenticate with administrator privileges to SmartConsole admin panels.

    Two weeks ago, the Dutch National Cyber Security Centre (NCSC-NL) also warned organizations to urgently patch two critical Check Point VPN flaws (CVE-2026-85102 and CVE-2026-85103) because it “expects exploitation attempts to occur soon.”

    More recently, on Friday, Check Point released security updates to address another critical authentication bypass (CVE-2026-16232) in the login process for Security Management Server and Security Gateways that lets attackers execute code with root privileges on management systems.

    While the company has not yet flagged CVE-2026-16232 as actively exploited, it said security teams can identify attacks by looking for “Administrator failed to log in: Username too long” alerts in the Audit and Admin login logs.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    attacks check Exploited management Point server warns ZeroDay
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Hackers start exploiting critical WordPress flaw for code execution

    Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape

    Anthropic and OpenAI Models Still Attempt Restricted Actions in Safety Tests

    545 Hackers Tested It First. Now XRanges for AI Scores Your Security Agent

    Djibouti’s Refugee Crisis: What to Know as Houthi Attacks Ramp Up

    New RemControl Android banking malware targets users in Europe and Canada

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Trump Administration Weighs Overseas Stablecoin Push

    September 24, 2026

    NASA Selects Far-Infrared Telescope as First in New Mission Class

    September 24, 2026

    A ‘devil-like’ flower from Thailand is new to science — and critically endangered

    September 24, 2026

    Germany Under Friedrich Merz Has Lost Its Authority at Home and Abroad

    September 24, 2026
    Latest Posts

    Ransom Cartel ransomware creator sentenced to 16 years in prison

    August 5, 2026

    Uber CEO brushes off reports of a Waymo break-up

    August 5, 2026

    Fauci Faces Contempt Vote. Here Are the Legal Issues Involved.

    August 6, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Trump Administration Weighs Overseas Stablecoin Push

    September 24, 2026

    NASA Selects Far-Infrared Telescope as First in New Mission Class

    September 24, 2026

    A ‘devil-like’ flower from Thailand is new to science — and critically endangered

    September 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.