

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Your Right to Know: Use of Signal app risks eroding trust

    November 2, 2026

    Human Error Is the AI Risk We Should Focus on Now

    November 2, 2026

    A decade of magical thinking since Brexit has taught me that it’s always OK to hope for better | Zoe Williams

    November 2, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Your Right to Know: Use of Signal app risks eroding trust
    • Human Error Is the AI Risk We Should Focus on Now
    • A decade of magical thinking since Brexit has taught me that it’s always OK to hope for better | Zoe Williams
    • BTCPay Server warns of hot wallet crypto thefts on outdated instances
    • Newborn survival improves when families receive financial support
    • Parents’ concerns to trigger urgent checks in A&E
    • Zanzibar’s seaweed farmers see better future through science and partnership (commentary)
    • Native American Remains Found in Organ Pipe Cactus National Monument Amid Border Wall Construction — ProPublica
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Monday, November 2
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    WeaselBiscuit Stealer Spreads via 13 npm Packages to Harvest Chrome Extension Storage

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 18, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananSep 18, 2026Malware / Web Security

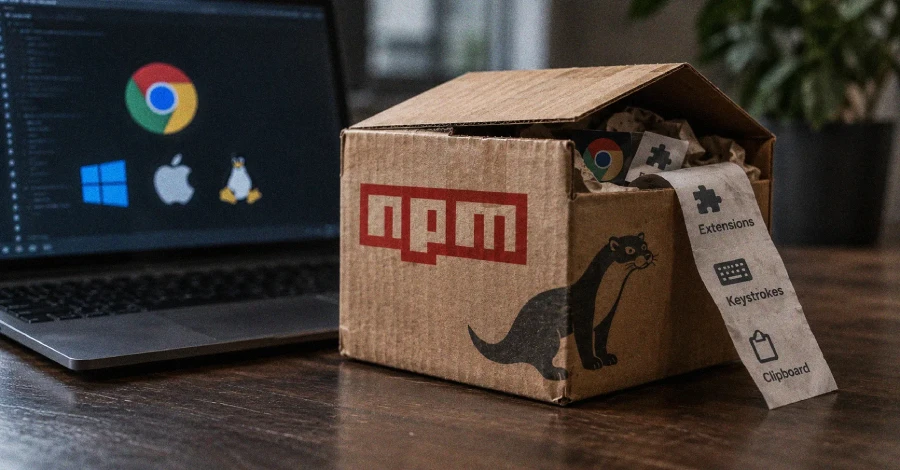
    Cybersecurity researchers have discovered a cluster of 13 npm packages that have been found to deliver a previously undocumented JavaScript stealer codenamed WeaselBiscuit.

    The new malware family, per OpenSourceMalware, exhibits functional overlaps with two malware strains associated with the Democratic People’s Republic of Korea’s (DPRK) Contagious Interview campaign: BeaverTail and OtterCookie. “It’s smaller, lighter, and stripped down, with many of the heavier functions removed entirely,” security researcher Paul McCarty (aka 6mile) said.

    The names of the packages are below –

    • @biz44/id10-client
    • @biz44/id12-client
    • @biz44/id44-client
    • @biz44/id79-client
    • @biz44/id95-client
    • @biz44/id99-client
    • @biz44/process-runtime-utils
    • @biz44/runtime-utils
    • engin1
    • id79-client
    • process-lhpm
    • process-mite
    • process-tailwind

    “It’s a stripped down stealer that borrows several functions from DPRK’s BeaverTail and OtterCookie, but is much smaller and self-contained,” Jenn Gile, co-founder of OpenSourceMalware, said in a statement shared with The Hacker News. “Hence the ‘WeaselBiscuit’ name, because a weasel is smaller than an otter, and we can argue that biscuits are less fancy than cookies.”

    Cybersecurity

    BeaverTail is the name assigned to a cross-platform information-stealing malware and downloader operated by North Korean threat actors behind Contagious Interview to target software developers, IT professionals, and cryptocurrency users. The malware has been active since at least late 2022.

    On the other hand, OtterCookie combines information-stealing capabilities with remote access functionality that allows the operators to execute commands on compromised hosts. The malware was first publicly documented by NTT Security Holdings in December 2024.

    WeaselBiscuit is notable for its simplicity, lacking remote access, persistence, cryptocurrency wallet-draining code, and the ability to deliver secondary payloads like InvisibleFerret. Instead, it’s triggered via an npm import, which causes the loader (“loader.js”) to pull the main malware from an Npoint dead drop and execute it directly in memory.

    Upon execution, it resolves its command-and-control (C2) configuration from a separate Npoint URL, profiles the compromised host, and harvests Chrome extension storage across Windows, macOS, and Linux. Based on operator commands received from the C2 server (“103.170.217[.]184:8787”), it can also log clipboard contents and keystrokes on Windows machines.

    “While this malware does not have the same crypto wallet stealer functions as its big siblings, the Chrome extension-storage capability is financially relevant: it can expose wallet-extension state or other extension-held sensitive data,” McCarty explained. “It uploads every readable, nonempty file under the extension’s Local Extension Settings directory — a raw LevelDB key/value store — wholesale.”

    OpenSourceMalware has emphasized that despite the “meaningful overlap with DPRK-associated Contagious Interview tooling,” there is no definitive evidence in terms of operator infrastructure, victimology, campaign metadata, or signing material to conclusively attribute it to North Korea.

    Cybersecurity

    Other tradecraft signals that point to North Korea are as follows –

    • The use of Npoint.io, a lightweight online JSON storage service, an aspect that was flagged by NVISO in November 2025 in connection with Contagious Interview
    • The use of nested public-IP and geolocation lookup via api.ipify.org and ip-api.com
    • Similarities in C2 architecture that overlap with OtterCookie
    • The use of a numerical campaign ID (10, 12, 44, 79, 95, 99) to tag each install, mirroring that of PolinRider

    If WeaselBiscuit does turn out to be the latest addition to DPRK’s malware arsenal, this wouldn’t be the first time the threat actors have attempted to merge the features of BeaverTail and OtterCookie. In October 2025, Cisco Talos said it identified an npm package named “node-nvm-ssh” that “had characteristics of BeaverTail and of OtterCookie, blurring the distinction between the two.”

    Chrome Extension Harvest npm Packages spreads Stealer storage WeaselBiscuit
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    BTCPay Server warns of hot wallet crypto thefts on outdated instances

    Cybersecurity M&A Roundup: 37 Deals Announced in October 2026

    DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment

    Hackers disrupt refrigeration systems at European supermarkets

    Over 1,000 GitLab servers vulnerable to ongoing RCE attacks

    Malicious Claude Code Extension Served in Cursor Supply Chain Attack

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Your Right to Know: Use of Signal app risks eroding trust

    November 2, 2026

    Human Error Is the AI Risk We Should Focus on Now

    November 2, 2026

    A decade of magical thinking since Brexit has taught me that it’s always OK to hope for better | Zoe Williams

    November 2, 2026

    BTCPay Server warns of hot wallet crypto thefts on outdated instances

    November 2, 2026
    Latest Posts

    Is the world experiencing more earthquakes now than before? | Earthquakes News

    August 17, 2026

    Disabled creatives like me are behind many of your favourite shows – so why has our work support been withdrawn? | Annalisa Dinnella

    August 17, 2026

    A little-known protein may be fueling Alzheimer’s — and scientists found a way to block it

    August 17, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Your Right to Know: Use of Signal app risks eroding trust

    November 2, 2026

    Human Error Is the AI Risk We Should Focus on Now

    November 2, 2026

    A decade of magical thinking since Brexit has taught me that it’s always OK to hope for better | Zoe Williams

    November 2, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.