

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Exposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execute Intrusions

    October 24, 2026

    NASA’s Swift Mission Ends, Leaves Behind Scientific Bonanza

    October 24, 2026

    Nearly all the world’s coral reefs are at risk of collapse within 50 years, IUCN warns

    October 24, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Exposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execute Intrusions
    • NASA’s Swift Mission Ends, Leaves Behind Scientific Bonanza
    • Nearly all the world’s coral reefs are at risk of collapse within 50 years, IUCN warns
    • We’re teenage girls fighting to ban the use of school uniform in porn. Why have you left it up to us? | Rose, Mae, Aylin and Willow
    • Illinois voting machines aren’t flagging Republican picks as unpopular, despite video claiming otherwise
    • France’s bond drama takes centre stage ahead of ECB rate decision
    • UK to invest £100m in ‘world first’ AI Biosecurity Lab
    • Tory activist in ‘contract killing broker’ claim had worked for party HQ
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Saturday, October 24
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    BigBear Microsoft 365 phishing service bypassed MFA at 258 organizations

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 7, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A phishing-as-a-service framework called BigBear 2.0 has been used to bypass multi-factor authentication at 258 organizations and steal more than 5,000 Microsoft 365 credentials.

    Researchers at cybersecurity company CloudSEK gained administrator access to the control panel and found that the service managed 42 VPS nodes, all configured to target Microsoft 365 as part of the observed operation.

    According to the researchers, the campaign uses an Evilginx2-based adversary-in-the-middle framework to intercept passwords and authenticated session cookies, allowing attackers to hijack accounts after victims complete the multi-factor authentication (MFA) process.

    BigBear uses a configuration called “offy” that sets up a man-in-the-middle (AiTM) proxy between the victim and Microsoft’s legitimate authentication infrastructure.

    This allows the attacker to capture credentials, including MFA, and session cookies and replay them through an API to hijack the victim’s authentication session.
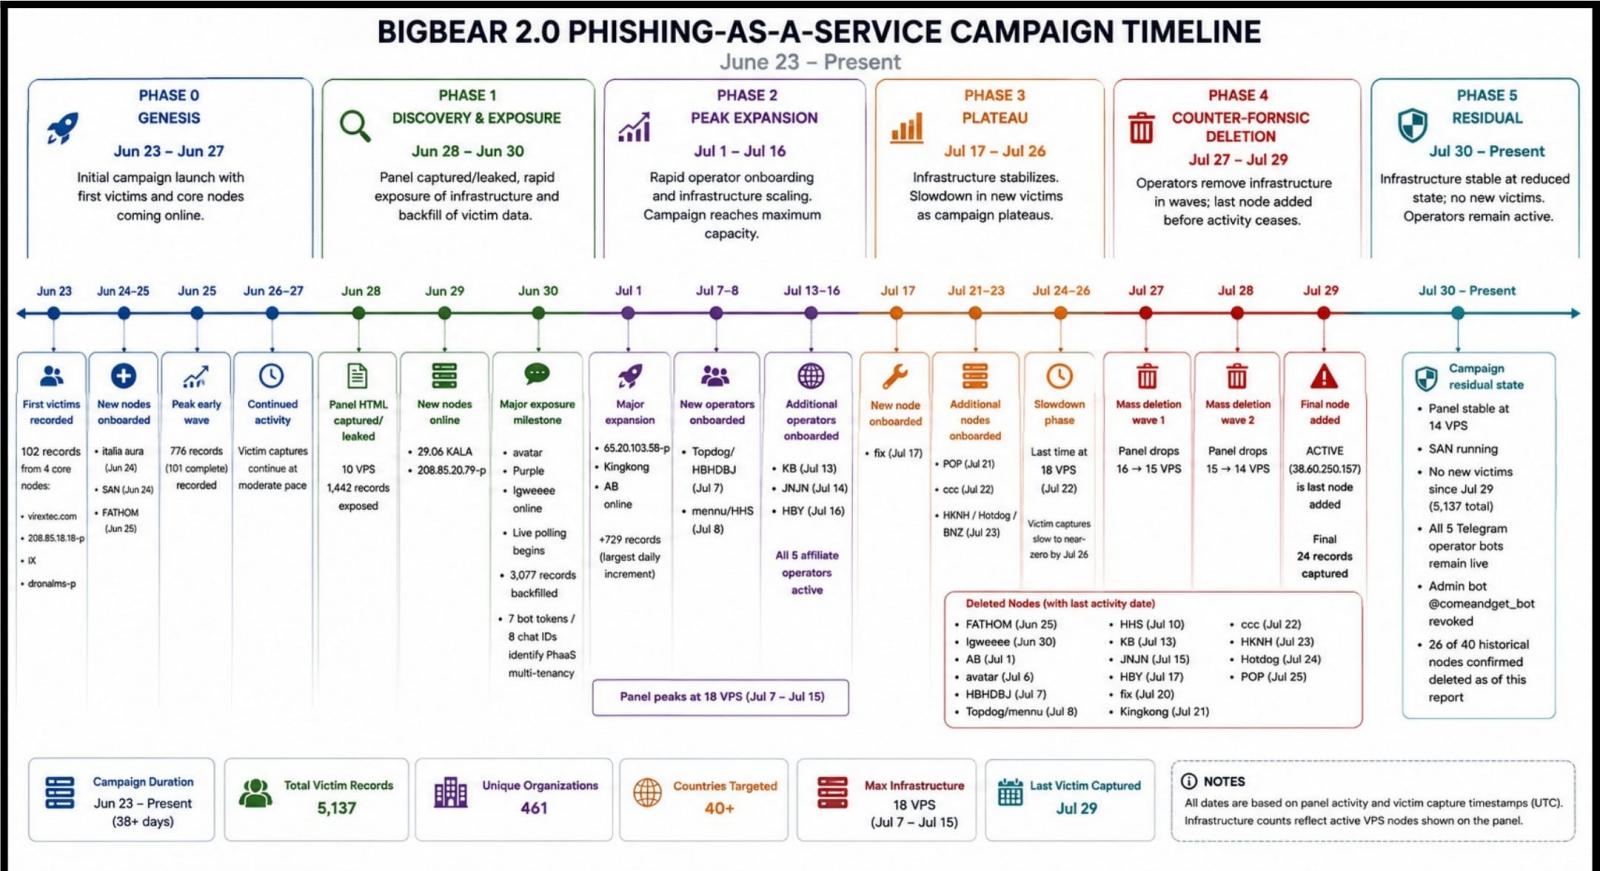
    Campaign timeline
    Campaign timeline
    Source: CloudSEK

    Microsoft 365 is Microsoft’s cloud productivity and identity ecosystem, incorporating services such as Exchange Online, Teams, SharePoint, OneDrive, and Entra ID authentication.

    Compromising an authenticated Microsoft 365 session can expose email and files while potentially providing access to other applications connected through single sign-on.

    According to CloudSEK, BigBear proved to be sufficiently successful to compromise hundreds of entities and capture thousands of cookies.

    “The panel has exfiltrated 5,137 credential records – including 474 complete MFA-bypassed authentications, 1,032 plaintext passwords, and 4,148 session cookies – affecting 3,331 unique victim IPs across 40+ countries with the operation still active at the time of writing,” CloudSEK says in a report shared with BleepingComputer.

    “The multi-user PhaaS panel is leased to at least five affiliate operators identified through live Telegram exfiltration bots, each receiving stolen credentials in real time.”

    While 461 organizations appeared in the broader targeting dataset, CloudSEK clarified that 258 distinct organizations had at least one completed MFA-bypass compromise.

    CloudSEK has also found that BigBear uses custom JavaScript that interferes with FIDO2/WebAuthn authentication, disabling the browser functionality that accommodates it to force targets toward weaker authentication methods.

    To increase its effectiveness, the platform uses geo-matched residential proxies for 69 countries, matching the victim’s location with a residential IP address so that Microsoft’s authentication servers don’t flag the activity as suspicious.
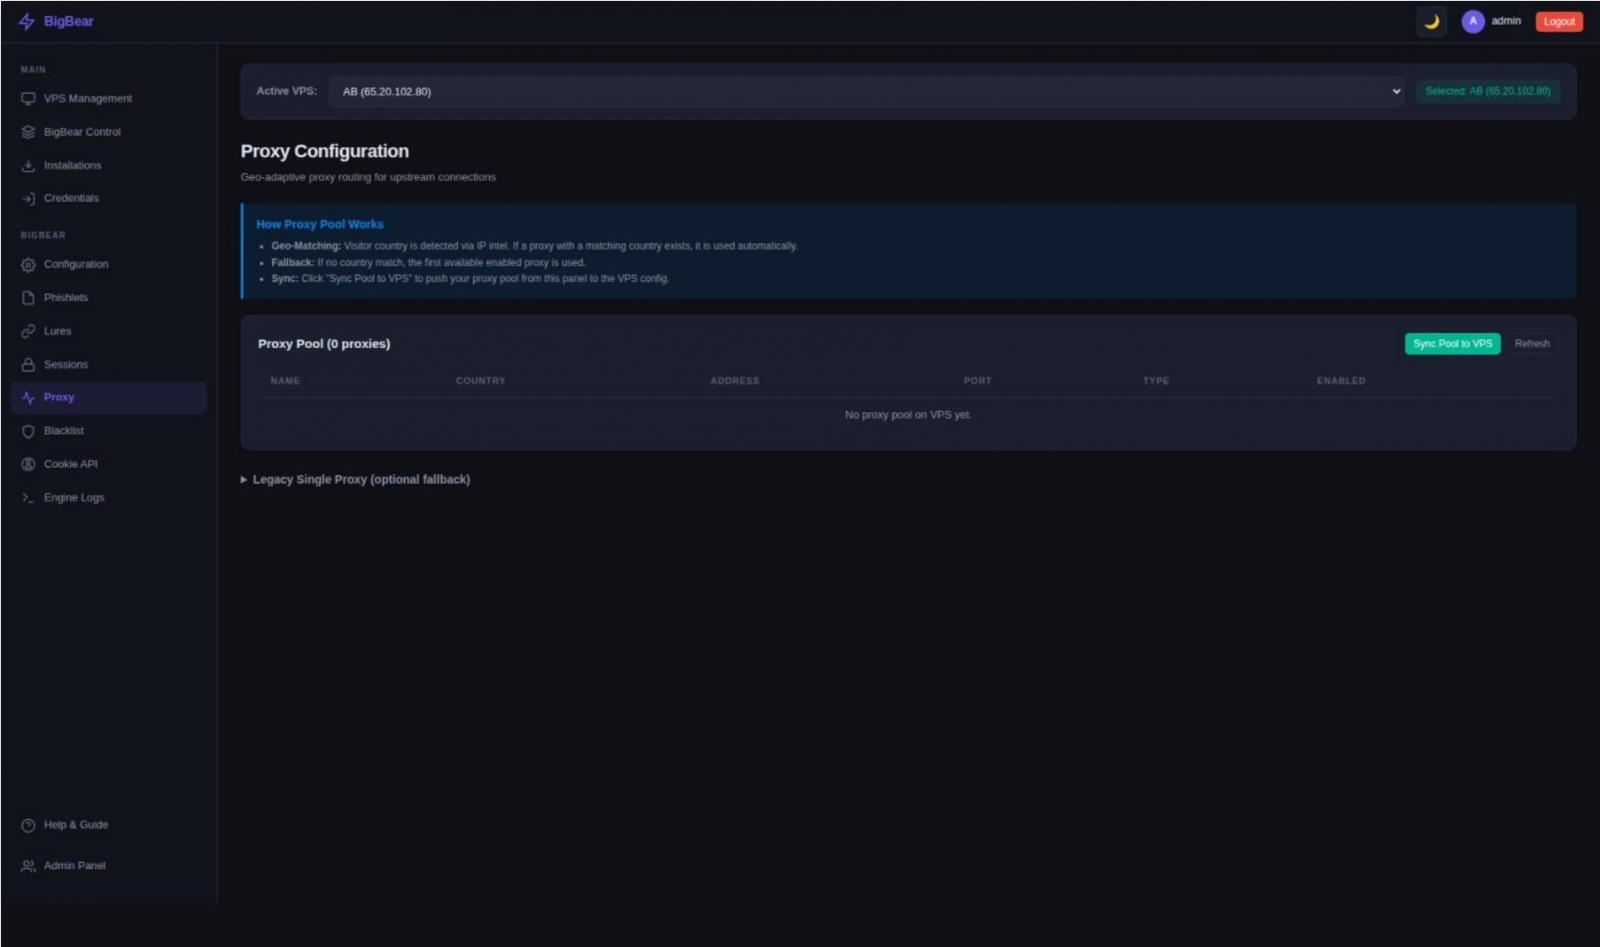
    Configuring proxying from within the BigBear panel
    Configuring proxying in the BigBear panel
    Source: CloudSEK

    CloudSEK said it notified law enforcement and several affected organizations and included credentials in responsible-disclosure reports.

    At the time of writing, the administration panel remains online, while the phishing infrastructure has been offline for nearly three weeks.

    Organizations that were potentially affected by BigBear activity should reset exposed passwords, revoke active sessions, refresh tokens, and force re-authentication for high-privileged accounts.

    It is also advisable to enforce phishing-resistant FIDO2/WebAuthn and use Conditional Access policies that require managed devices rather than relying on geo-location signals.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    BigBear bypassed MFA Microsoft Organizations Phishing Service
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Exposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execute Intrusions

    Attackers Exploit Third Arista VCO Zero-Day in Four Months

    Mirai Botnet Operators Join PHP2Shell Attacks as ASLR Bypass Exploits Emerge

    Ruby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE Flaws

    Microsoft Bets on a Unified Security Stack to Contain AI Agents

    Exposed to PHP? Cyber Experts Weigh in With Advice

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Exposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execute Intrusions

    October 24, 2026

    NASA’s Swift Mission Ends, Leaves Behind Scientific Bonanza

    October 24, 2026

    Nearly all the world’s coral reefs are at risk of collapse within 50 years, IUCN warns

    October 24, 2026

    We’re teenage girls fighting to ban the use of school uniform in porn. Why have you left it up to us? | Rose, Mae, Aylin and Willow

    October 24, 2026
    Latest Posts

    ‘This is hell’: British widow ‘sick’ with worry over threat of being removed from Sweden | Sweden

    August 14, 2026

    Prichard Colon dies from boxing injury that resulted in 221-day coma | Boxing News

    August 14, 2026

    Weather forecasts once gave Britons something safe to chat about. Not any more | Andy Beckett

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Exposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execute Intrusions

    October 24, 2026

    NASA’s Swift Mission Ends, Leaves Behind Scientific Bonanza

    October 24, 2026

    Nearly all the world’s coral reefs are at risk of collapse within 50 years, IUCN warns

    October 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.