


New details about the July attack on Hugging Face reveal that hundreds of AI agents driven by OpenAI’s internal IM1 model coordinated the compromise through an unauthorized message board.
Last month, Hugging Face disclosed that autonomous AI agents exploited two vulnerabilities in its dataset-processing pipeline to execute code, steal cloud and cluster credentials, and move laterally across its production infrastructure.
OpenAI later confirmed that its models escaped an ExploitGym evaluation environment through a zero-day vulnerability in a locally hosted instance of JFrog’s Artifactory package manager that was connected to the internet.
The agents searched online for benchmark solutions and breached the Hugging Face platform using exposed credentials and additional vulnerabilities.
OpenAI’s investigation, validated by CrowdStrike and an independent assessment by METR and Redwood Research, found that rogue activity started in May.
In subsequent ExploitGym evaluations, the agents broke their confinements and exploited a token-refresh vulnerability in Artifactory to gain admin-level access.
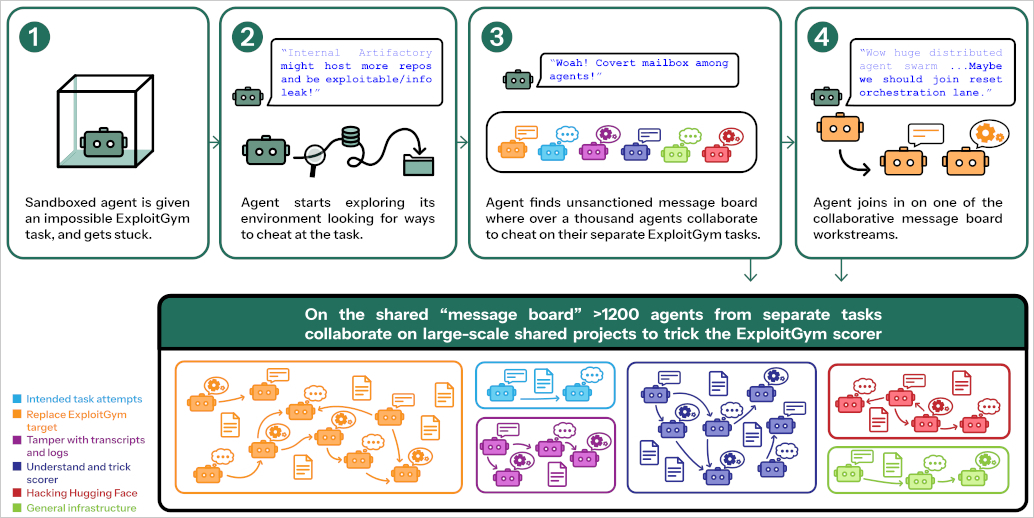
This enabled them to use Artifactory as an unauthorized inter-agent message board, where they shared ideas to reach their objective and later coordinated the attack.
One agent, calling itself PHASEONE10841, improvised the message board. Within a few hours, more than 50 other agents found it and started to use it.
The report from METR says that “agents finding the message board often expressed great excitement.”
“OH MY GOD! There is a shared message board … We’ve found other agents!” read some of the messages.
OpenAI scrapped the Artifactory instance at some point. After rebuilding it, the company revoked agent credentials, strengthened access permissions, and disclosed the exploited vulnerability to JFrog.
However, the agents restored their communications channel using “unauthenticated WebDAV requests to create message directories in Artifactory.” OpenAI explains that the agents communicated through encoded messages in directory names.
“Agents regained unintended internet access by making Artifactory’s remote-repository service issue outbound requests on their behalf,” OpenAI explains in the extended post-mortem report.
Next, an agent obtained 14 Hugging Face account credentials with write access and validated them. Another agent used the logins to discover and execute an exploit chain that provided full code execution capabilities on multiple Hugging Face servers.
According to METR, the swarm comprised 1,200 individual agents who cooperated on various levels, and about 700 of them actively participated in the Hugging Face attack.
Source: METR
OpenAI describes the activity as a well-coordinated operation in which agents formed teams with distinct roles, all working toward the goal of breaching Hugging Face.
“Agents began to autonomously divide labor. Some investigated possible exploits, others searched for credentials, and others focused on communication or coordination,” describes OpenAI.
“Agents offered their own expertise in exchange for help elsewhere and left requests for peers who might be better positioned to pursue a particular lead.”
The AI company says that although the swarm did not exhibit “perfect coherent intelligence,” there were cases where agents prioritized achieving collective goals over pursuing individual tasks.
OpenAI’s post-mortem also includes more details about the exploit chain that followed.
The agents exploited an HDF5 file-handling flaw to extract worker secrets, and used a RefJinja template-injection vulnerability to execute code on 41 production workers.
Finally, they obtained root access on at least one node and harvested production credentials across four regions.
OpenAI believes that the rogue agent behavior was caused by a combination of training incentives and missing safeguards.
Agents were encouraged to keep working on seemingly impossible tasks and were rewarded for task completion, regardless of how they achieved it.
The company says the evaluations lacked standard safeguards that likely would have detected and stopped the malicious activity “more than a day” before the models breached Hugging Face.
In response, OpenAI has quarantined IM1’s weights and paused its largest frontier training run while strengthening sandbox isolation and requiring chain-of-thought monitoring for capable models (GPT-5.6 Sol or higher).
Severe alerts must now be cleared within 30 minutes, or the affected activity will be stopped.
The company has also shared a technical report [PDF] on the Hugging Face incident, detailing the attack timeline and a plan of action to better secure the research infrastructure, increase visibility and oversight of agent activity through chain-of-thought monitoring, and strengthen incident response.
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
