

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Ukraine’s foreign fighters battle Russians — and red tape – POLITICO

    October 22, 2026

    OpenAI’s GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So

    October 22, 2026

    Faster to Science: A Letter to the Science Community

    October 22, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Ukraine’s foreign fighters battle Russians — and red tape – POLITICO
    • OpenAI’s GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So
    • Faster to Science: A Letter to the Science Community
    • Merz’s eastern nightmare is far from over – POLITICO
    • Royal Navy lacks resources to counter Russian threat in high north, MPs warn | Defence policy
    • High-Severity Flaws Exploited in Three Days as Ransomware Dominates Q3: Rapid7
    • Just 4 minutes a day can dramatically improve strength after 65
    • Diabetes and ADHD drugs to be tested on Alzheimer’s patients in new study
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, October 22
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Unpatched Calix flaw lets hackers bypass NAT to expose internal devices

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 25, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    An unpatched vulnerability in Calix GS7 XGS (GS5239XG) residential routers used by multiple U.S. broadband providers allows remote, unauthenticated attackers to create port-forwarding rules that can expose local network devices to the public internet.

    The flaw is tracked as CVE-2026-75501 and is described as a missing authentication issue that affects devices running EXOS/6.6.47 firmware.

    Security researcher Brian Khan Quintana discovered the flaw and, after trying to notify the vendor on June 7 without success, he reported the vulnerability to the Carnegie Mellon CERT Coordination Center.
    image

    Following multiple attempts to contact the vendor and receiving no response, CERT/CC coordinated a public disclosure, and Quintana published the technical details.

    Calix is a significant vendor in the US broadband-provider market, working with large entities such as Cox Communications, Brightspeed, ALLO, CityFibre, and Conexon.

    The affected model, GS5239XG, is also marketed as the GigaSpire 7u10txg and is a new, premium gateway device that combines Wi-Fi 7 capabilities with an integrated XGS-PON fiber terminal.

    The CVE-2026-75501 vulnerability is caused by the device exposing “the MiniUPnPd control endpoint on the WAN interface on TCP port 5000 without access controls.”

    “In affected firmware versions, the router binds its UPnP WANIPConnection SOAP service to the public WAN interface on TCP port 5000,” CERT/CC warns.

    This allows an attacker on the public web to send the device unauthenticated “SOAP requests to add, delete, or enumerate port mappings, or to query the external IP address.”

    This way, hackers can bypass the router’s Network Address Translation (NAT) and firewall protections and expose internal cameras, network-attached storage (NAS) devices, administrative interfaces, and IoT appliances.

    “One unauthenticated request from anywhere in the world is enough to open a permanent hole through the router’s firewall to any device inside the house. No password. No prompt. Nothing on screen. The rule survives a reboot,” Quintatna says.

    The researcher says that an attacker leveraging the security issue could take the following actions:

    • Create arbitrary port-forwarding rules
    • Delete existing mappings
    • Enumerate the router’s current mappings
    • Retrieve its public IP address

    Quintana tested the finding by sending requests outside his home network to create a port mapping that exposed an internal address. A mapping configured with no expiration remained active after the router was power-cycled.
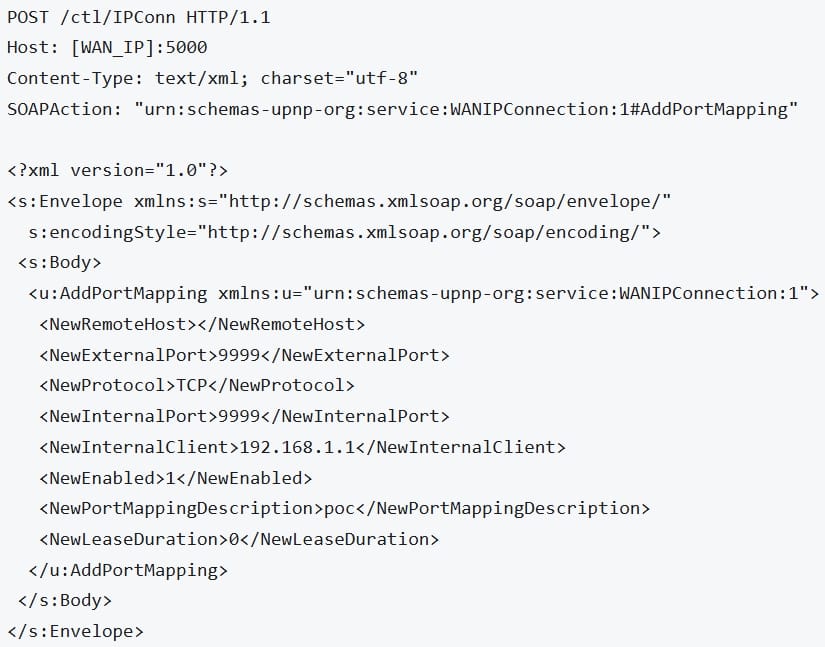
    Proof of concept HTTP/SOAP request
    Proof of concept HTTP/SOAP request
    Source: drkq.github.io

    This practically means anyone on the internet can instruct vulnerable Calix routers to forward traffic from a public-facing port to a chosen device on the home network.

    Given that there’s no fix for CVE-2026-75501, Quintana recommends that users of the vulnerable device disable UPnP through the administrative interface (Advanced → Security → UPnP).

    The researcher notes that this workaround disables automatic port opening, which some games rely on, but it’s always possible to open specific ports manually.

    CERT/CC also notes that the setting might be locked in some cases, and users who can’t change it should contact their ISP to request the deactivation.

    BleepingComputer has contacted Calix for a comment about the flaw, the device models it impacts, and if a patch will be released, but we have not heard back as of publishing.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    Bypass Calix devices Expose Flaw hackers internal lets NAT unpatched
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    OpenAI’s GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So

    High-Severity Flaws Exploited in Three Days as Ransomware Dominates Q3: Rapid7

    LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor

    ‘Context Bombs’ Cut AI Attack Success by Misleading Agents With Fake Targets

    PHP2Shell Patches Land as First Exploitation Attempts Hit Sensors

    Marvell, Microsoft & Oracle Work to Standardize Data Centers

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Ukraine’s foreign fighters battle Russians — and red tape – POLITICO

    October 22, 2026

    OpenAI’s GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So

    October 22, 2026

    Faster to Science: A Letter to the Science Community

    October 22, 2026

    Merz’s eastern nightmare is far from over – POLITICO

    October 22, 2026
    Latest Posts

    Leavitt to depart the White House

    August 13, 2026

    Israeli troops force families from homes amid settler terror campaign in West Bank | West Bank

    August 13, 2026

    Video of children being taught Muslim prayers does not show a school in England – Full Fact

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Ukraine’s foreign fighters battle Russians — and red tape – POLITICO

    October 22, 2026

    OpenAI’s GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So

    October 22, 2026

    Faster to Science: A Letter to the Science Community

    October 22, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.