


Cryptocurrency hardware wallet provider SafePal is warning of a data breach affecting about 39,798 customers after a flaw was exploited to steal customer order information, and a threat actor is now claiming to be selling the stolen data.
SafePal says the breach impacts customers who placed orders between March 2, 2025, and April 11, 2026, exposing their names, email addresses, shipping addresses, phone numbers, and purchase information.
The company says the breach did not expose customers’ wallet seed phrases, private keys, passwords, bank account information, payment card numbers, government-issued identification numbers, or other credentials.
“No evidence has been found that the incident itself compromised access to SafePal wallets or funds,” SafePal said in a security advisory published Sunday.
The company says it notified all impacted customers via email on August 16 with the subject “[Important] Your SafePal Order Information Has Been Affected.”
SafePal has also launched an online verification tool that lets customers enter their order number and shipping country to determine whether the details of that order were stolen.
The company warns that the stolen information could be used to conduct targeted phishing and other social engineering attacks, with customers reporting SafePal phishing emails and phone calls as early as May.
Order-tracking flaw exposed customer data
A threat actor now claims to be selling the stolen SafePal customer data on a cybercrime forum.
As spotted by DarkWebInformer, the seller referenced the same affected order period and approximately 39,798 customers disclosed by SafePal.
For potential buyers, the threat actor is also willing to share order ID and shipping country information from stolen orders, which can be confirmed on SafePal’s online verification tool as proof that the sale is legitimate.
“Not interested in low balls , please come correct and with a good price or do not message me at all,” reads the forum post.
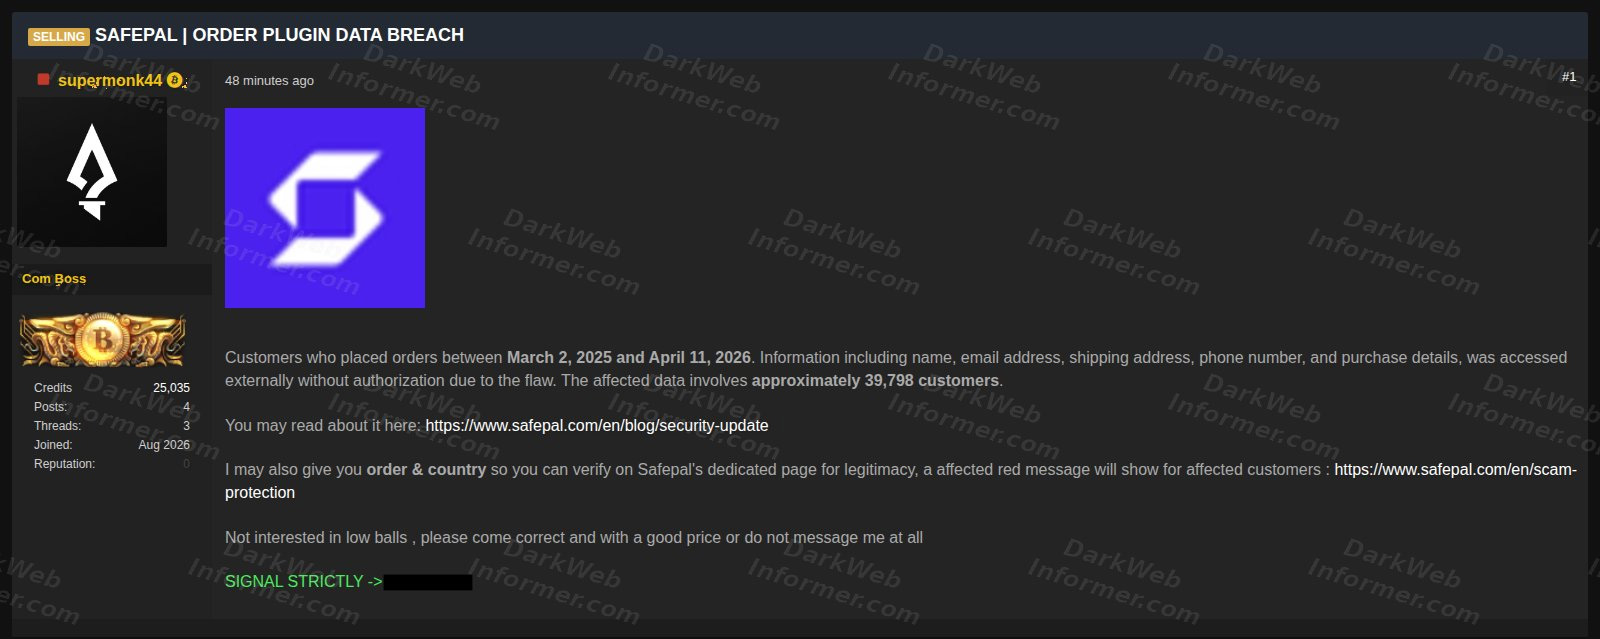
Source: DarkWebInformer
BleepingComputer has not independently verified that the threat actor possesses the stolen data.
SafePal says it first received a report consistent with the incident in early May 2026, which it initially treated as an isolated case.
While it is unclear whether this report is related, a customer posted on X that they received a SafePal phishing email and a phone call from someone claiming to be a company employee in May. The phishing email claimed that a security vulnerability had been discovered in the SafePal X1 hardware wallet and that a firmware update was required to fix the flaw.
“We first received a report consistent with this issue in early May, and treated it as an isolated case at the time, but escalated it into a formal security investigation and introduced additional protections,” reads the advisory.
“As our e-commerce system involves multiple interconnected components and external integrations, as well as third-party logistics partners, we could not immediately rule out several possible explanations.”
In July, SafePal began what it described as a “full review and rebuild” of its order-processing system and discovered an authorization flaw in the order-tracking function of a plug-in that allowed unauthorized access to another customer’s order information.
SafePal says it fixed the vulnerability and implemented additional security measures. The company is also working with a third-party security firm to validate the fix and conduct a broader review of its order-processing systems.
However, as part of this investigation, SafePal determined that a threat actor exploited the flaw to steal order information belonging to approximately 39,798 customers.
During the investigation, SafePal also discovered a separate configuration error that caused a data-cleanup process to stop functioning correctly between September 2025 and April 2026, resulting in order data being retained as far back as March 2025.
For affected orders, SafePal says it has purged personal data from active e-commerce servers, although it is retaining an encrypted offline copy for potential law-enforcement investigations.
SafePal also warns customers to watch for targeted phishing emails and phone calls about firmware upgrades, product returns, refunds, or legal investigations.
The company says it has already taken down more than 30 fraudulent websites and phishing links tied to this incident.
Customers whose order information was exposed do not need to replace their hardware wallets or move cryptocurrency because of the breach, according to SafePal.
However, if a customer already shared their seed phrases or private key in response to a phishing email or text, they should treat their wallet as compromised and transfer any assets to a new wallet on a trusted SafePal device or official application.
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
