

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Cosmos restarted to seize $2.2 million in stolen ATOM, but 169,000 tokens still escaped

    September 24, 2026

    Elephants treat themselves with medicinal plants, witnesses say

    September 24, 2026

    Fat Bear Week opens for Alaska’s heavyweight crown. Can Chunk, the 1,200-pound champ, win again?

    September 24, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Cosmos restarted to seize $2.2 million in stolen ATOM, but 169,000 tokens still escaped
    • Elephants treat themselves with medicinal plants, witnesses say
    • Fat Bear Week opens for Alaska’s heavyweight crown. Can Chunk, the 1,200-pound champ, win again?
    • Tom Watson’s move to Palantir is the latest sign of how far the rot has spread in UK politics | Clive Lewis
    • Russia slams Kyiv with ballistic missiles as Ukrainians brace for harsh winter
    • Is Burnham right to blame Russia for spreading online disinformation?
    • Holborn and St Pancras: 15 candidates in race to replace Starmer
    • The Global Story – Is a free press at serious risk in Trump’s America?
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, September 24
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    New NatJack Attacks Hijack TCP Sessions and Spoof DNS by Manipulating NAT Tables

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 9, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Swati KhandelwalAug 07, 2026Network Security / Vulnerability

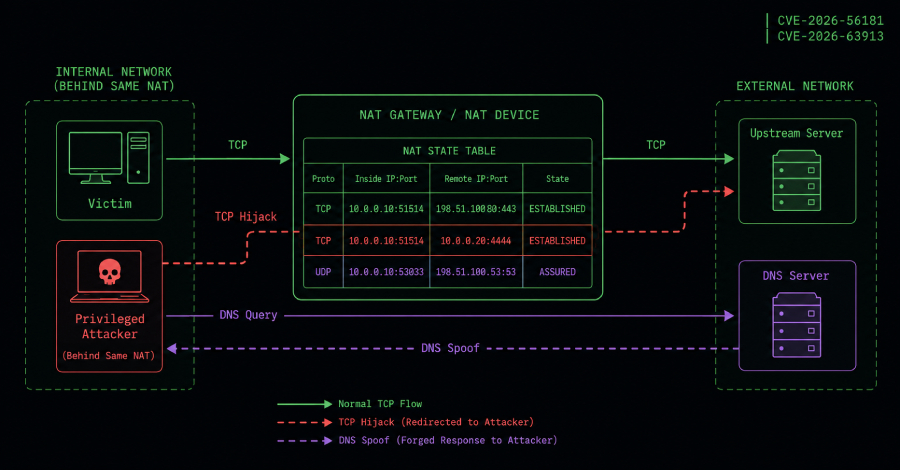
    Security researcher Malcolm Stagg has disclosed a new attack class called NatJack that manipulates network address translation (NAT) connection state to hijack active TCP sessions, spoof DNS responses, expose mapped ports, and exhaust NAT tables.

    Presented at Black Hat USA 2026, the research found affected behavior across independently developed implementations, including Windows and Linux.

    Two implementation-specific flaws have been assigned CVEs: CVE-2026-56181 (CVSS score: 8.3) in Windows NAT used by Hyper-V, and CVE-2026-63913 (CVSS score: 8.2) in Linux Netfilter conntrack.

    NatJack generally requires the attacker to have privileged access to a system behind the same NAT as the victim. The mitigation guidance therefore emphasizes separating untrusted workloads from trusted systems that share NAT infrastructure.

    Cybersecurity

    There is no single patch for the broader attack class. Organizations should apply available Windows and Linux updates and encrypt traffic even within internal networks. The research also recommends Internet Protocol (IP) Source Guard where applicable.

    The NatJack research, conducted independently by Stagg through SODIUM-24, targets an assumption built into many NAT implementations: hosts behind the same NAT are generally assumed not to manipulate one another’s connection state. An attacker controlling a system behind the same NAT can, depending on the implementation, manipulate connection-tracking entries belonging to another system.

    The research describes four main paths. One can redirect traffic from an active TCP connection by replacing its NAT mapping. Another interferes with a victim’s DNS request so the legitimate DNS response reaches the attacker, allowing a forged response to be sent back.

    Other techniques disclose externally mapped ports or fill the NAT connection table with spoofed flows until legitimate clients cannot create new connections.

    Synack said Stagg tested the techniques against dozens of real-world network infrastructure products from multiple vendors and demonstrated proof-of-concept exploitation in a controlled environment.

    The NatJack site does not publish a complete product-by-product matrix. The Hacker News found no public evidence that NatJack techniques have been exploited in the wild as of August 7, 2026.

    Cybersecurity

    For Linux, the kernel.org CNA record says a crafted SYN followed by a reset packet with an invalid sequence number can prematurely force an active Netfilter NAT entry into a closed state because the conntrack logic failed to validate its direction. Fixed stable releases include 5.10.259, 5.15.210, 6.1.176, 6.6.143, 6.12.93, 6.18.35, 7.0.12, and 7.1.

    Stagg says the kernel change fixes the code flaw but only mitigates the broader downstream-spoofing technique, increasing attack complexity rather than fully addressing it.

    Microsoft’s CNA record describes the Windows issue as an origin-validation error that enables spoofing from an adjacent network. Affected releases include Windows 11 24H2 before 26100.8875, 25H2 before 26200.8875, 26H1 before 28000.2525, and Windows Server 2025 before 26100.33158.

    NatJack also builds on earlier research into NAT-state manipulation. An NDSS 2024 study demonstrated TCP hijacking through NAT mapping manipulation and found 52 of 67 tested routers susceptible to its attack, work that produced ten CVEs.

    attacks DNS hijack Manipulating NAT NatJack Sessions Spoof Tables TCP
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    OT Security Guidance: NIST Drafts Updated Guide, CISA/FBI Advise on ICS Integrators

    OpenAI Agent Bypassed Australian Medicare Portal Controls to Access Non-Public Files

    58 hardware vulnerabilities: A guide to the threats

    Critical WordPress Vulnerability Exploited Immediately After Disclosure

    Hackers start exploiting critical WordPress flaw for code execution

    Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Cosmos restarted to seize $2.2 million in stolen ATOM, but 169,000 tokens still escaped

    September 24, 2026

    Elephants treat themselves with medicinal plants, witnesses say

    September 24, 2026

    Fat Bear Week opens for Alaska’s heavyweight crown. Can Chunk, the 1,200-pound champ, win again?

    September 24, 2026

    Tom Watson’s move to Palantir is the latest sign of how far the rot has spread in UK politics | Clive Lewis

    September 24, 2026
    Latest Posts

    Ransom Cartel ransomware creator sentenced to 16 years in prison

    August 5, 2026

    Uber CEO brushes off reports of a Waymo break-up

    August 5, 2026

    Fauci Faces Contempt Vote. Here Are the Legal Issues Involved.

    August 6, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Cosmos restarted to seize $2.2 million in stolen ATOM, but 169,000 tokens still escaped

    September 24, 2026

    Elephants treat themselves with medicinal plants, witnesses say

    September 24, 2026

    Fat Bear Week opens for Alaska’s heavyweight crown. Can Chunk, the 1,200-pound champ, win again?

    September 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.